What Documents Should Businesses Prepare for an Anti-Bribery Management Audit?
Learn which documents businesses should prepare for an anti-bribery management audit, from policies and risk assessments to records and compliance evidence.
 sahana sana
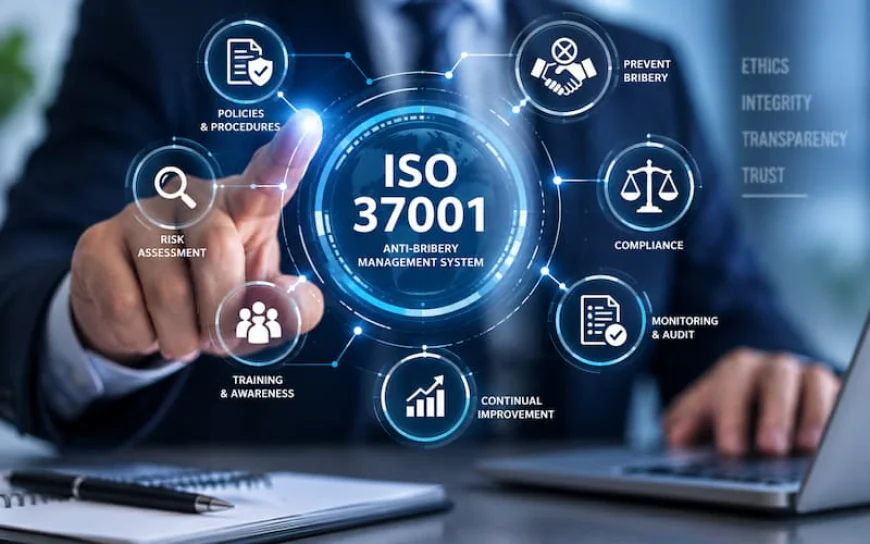
The business world is very competitive, and business transparency and ethical behavior are the keys to success in the long-run. The risk of bribery may vary among organizations that engage with customers, suppliers, government authorities, agents and the business partners. An effective anti-bribery management system assists the business to identify such risks, put in place effective controls and foster ethical behaviour within the organization. Anti-Bribery Management Audit gives a chance to evaluate the presence of the proper implementation of these controls, as well as supported with reliable documented information.
 The audit process can be more organized and effective by preparing the appropriate documents. The evidence that auditors normally seek is that the anti-bribery policies adopted by an organization are not merely written but also being applied in the day to day activities of the organization. The businesses intending to be iso 37001 certification in saudi arabia must have clear records that will record the risk assessment, Employee training, Third-party due diligence, financial controls, reporting processes, internal auditing, and management review. Effective documentation shows accountability and assists organizations in recognizing gaps prior to their impact on performance related to compliance.
1. Anti-Bribery Policy
One of the most significant documents that an organization should have is the anti-bribery policy. It ought to have a clear message of how the company is determined to stop bribery and encourage ethical business conduct.
The policy ought to broadly cover:
-
Ban of bribery and corruption.
-
Adherence to the relevant laws.
-
Employee responsibilities
-
Management commitment
-
Reporting requirements
-
Consequences of violations
-
Commitment to continual improvement
Gifts policy, hospitality policy, conflict of interest policy, donations policy and sponsorships policy and facilitation payment policies should also be kept where necessary.
2. Bribery Risk Assessment Records
Companies are obliged to record the process of detecting and assessing risks of bribery. The geographical location, business sectors, government interactions, third-party relationships, procurement activities, and high-risk transactions are some of the factors that should be taken into consideration in the risk assessment.
Records should show:
-
Identified bribery risks
-
Risk evaluation methodology
-
Risk ratings
-
Existing controls
-
Additional actions required
-
Responsible personnel
-
Review dates
It is worthwhile to regularly revise the risk assessment in case of any major alteration in business operations or other external needs.
3. Employee Training Records
Employees should be made aware of the anti-bribery provisions in the organization, and their respective obligations. The evidence of training and awareness programs should therefore be maintained by the businesses.
Useful records include:
-
Training schedules
-
Presentation and materials of training.
-
Attendance records
-
Employee acknowledgments
-
Assessment results
-
Awareness communications
The procurement, sales, finance, compliance and government facing employees might need further training depending on their roles and exposure to risk.
4. Third-Party Due Diligence Documents
There is a high potential of bribery by a third party. Organizations are expected to keep the due diligence records of agents, consultants, suppliers, distributors, contractors and other business partners.
Such documents can be:
-
Due diligence questionnaires
-
Background screening results
-
Risk assessments
-
Approval records
-
Ownership information
-
Compliance declarations
-
Anti-bribery commitments
-
Periodic monitoring records
Due diligence should be based on the risk posed by each third party.
5. Contracts and Agreements
Contracts should have the right anti-bribery requirements where necessary and the businesses must uphold them. Contracts with business partners could contain provisions regarding the adherence to the relevant legislation, bribery, audit, reporting, and dismissal in case of severe offences.
Through these documents, it is possible to show that the anti-bribery expectations are shared with outside parties and included in the business relationships.
6. Gifts, Hospitality, and Donation Records
There may be a conflict of interest or bribery risk, which occurs as a result of gifts and hospitality. Registers and approval records should be maintained by organizations on gifts, hospitality, charitable donations, sponsorship and other such activities.
It should be recorded that:
What was received/given.
-
The value involved
-
Relevant parties
-
Business purpose
-
Approval status
-
Time of the activity.
Reporting requirements and distinct approval limits would assist the employees in taking these activities in charge.
7. Financial and Procurement Records
Financial controls are critical in hindering unwarranted payments and distorted transactions. Auditors can check financial and procurement documents to ascertain whether transactions are duly authorized and documented.
Important records can consist of:
-
Invoices
-
Purchase orders
-
Expense claims
-
Payment approvals
-
Commission records
-
Vendor information
-
Procurement approvals
-
Segregation-of-duty records
It is important that organizations make sure that financial records are accurate, traceable and controlled.
8. Whistleblowing and Investigation Records
A good anti-bribery mechanism must offer appropriate avenues where employees and other stakeholders can report issues. Companies ought to have recorded protocols of receiving, evaluating, investigating and fixing reports.
Records may include:
-
Reporting procedures
-
Registers of complaint or report.
-
Investigation records
-
Investigation outcomes
-
Corrective actions
-
Follow-up activities
The information that is sensitive must be secured and only accessed by the appropriate people.
9. Internal Audit and Management Review Records
The records of internal audit reveal that the organization conducts periodic reviews of its effectiveness in anti-bribery measures. Audit plans, checklists, findings, nonconformities, corrective actions and follow-up evidence should be maintained by the businesses.
The management review records should also show that the top management reviews the performance of the anti-bribery management system. Such reviews can include audit findings, risk developments, incidents, compliance performance, corrective measures and opportunities to improve.
To organizations looking to iso 37001 certification in saudi arabia, the records may be of a great help in demonstrating management involvement and on-going improvement.
10. Corrective Action and Document Control Records
In the event that an organization has detected a weakness or nonconformity, then it must record the remedy that has been taken to address the problem. Records on corrective action must have the problem, root cause, action to be taken, the responsible individual, date of completion and verification of effectiveness.
Businesses must also have proper document control procedures that addresses approval, version control, updates, access, retention and disposal. The up-to-date versions of the relevant policies and procedures should always be made available to the employees.
How to Prepare for the Audit
Businesses are advised to go through their documentation prior to the audit, instead of coming up with records at the last minute. Internal audit can be done by a mere look around to locate missing or obsolete documents.
Organizations should:
-
Review their anti-bribery policy.
-
Revise the bribery risk assessment.
-
Check employee training records.
-
Check third party due diligence files.
-
Compliance clauses and check contracts.
-
Discuss financial and procurement controls.
-
Check records of reporting and investigation.
-
Audit internal audit.
-
Close outstanding corrective actions.
-
Make sure that documents are orderly and readily available.
Conclusion
Effective documentation is essential for demonstrating that an organization’s anti-bribery controls are properly established and implemented. Important evidence of compliance is present in policies, risk assessments, training records, third-party due diligence, contracts and financial records, investigation reports, internal audits and management reviews. A properly developed Anti-Bribery Management Audit can also aid companies in pinpointing the areas of weakness and enhance their overall compliance system.
The organizations are therefore advised to look at documentation as a continuous process of management and not as a process that has to be done at the end of the year. Having proper and up to date records enhances transparency, accountability and confidence of the stakeholders. Companies aiming at obtaining iso 37001 certification in saudi arabia may enjoy a structured method of integrating documented process with real business operations and promoting a constant enhancement.