How Do Hardware Wallet Phishing Scams Work, and Which Warning Signs Should You Never Ignore?
Hardware wallets are designed to keep your cryptocurrency safe, but they cannot protect you from every online scam. Phishing attackers use fake websites, emails, messages, and wallet update alerts to trick users into revealing their recovery phrases or connecting to malicious websites. One wrong step can put your crypto assets at risk, even when you own a trusted hardware wallet. Understanding the warning signs is an important part of Trezor phishing attack crypto wallet security. From fake support messages to suspicious firmware updates, knowing how these scams work can help you avoid costly mistakes. So, what should you look for before trusting a wallet-related message or website? Let's explore the common warning signs and the simple precautions that can help protect your cryptocurrency.
 Tom N
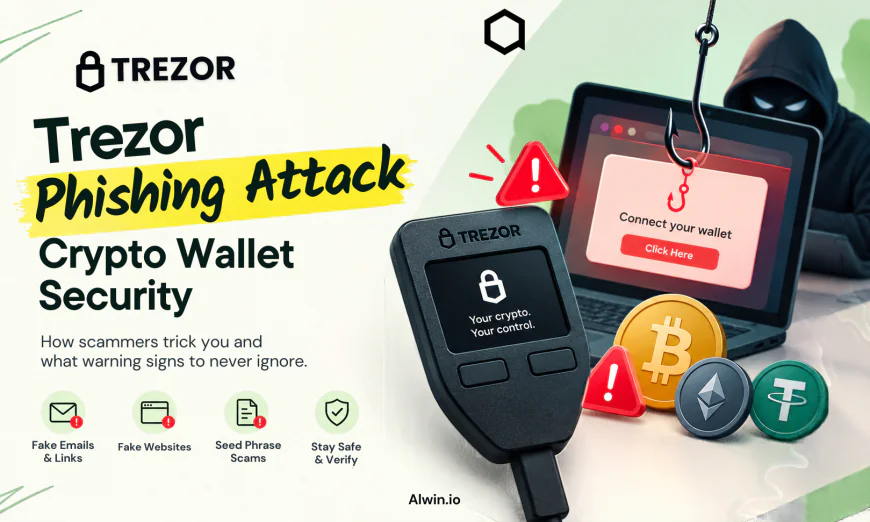
Hardware wallets are designed to keep your cryptocurrency safe, but they cannot protect you from every online scam. Phishing attackers use fake websites, emails, messages, and wallet update alerts to trick users into revealing their recovery phrases or connecting to malicious websites. One wrong step can put your crypto assets at risk, even when you own a trusted hardware wallet.
Understanding the warning signs is an important part of Trezor phishing attack crypto wallet security. From fake support messages to suspicious firmware updates, knowing how these scams work can help you avoid costly mistakes. So, what should you look for before trusting a wallet-related message or website? Let's explore the common warning signs and the simple precautions that can help protect your cryptocurrency.
What Is a Trezor Phishing Attack?
A Trezor phishing attack is a scam designed to trick cryptocurrency users into sharing sensitive wallet information or approving unsafe actions. Attackers may create fake Trezor websites, send fraudulent emails, or impersonate customer support to steal recovery phrases and gain access to crypto assets.
For better Trezor phishing attack crypto wallet security, always verify the website before entering information or connecting your hardware wallet. Never share your recovery seed phrase with anyone, including someone claiming to be from Trezor support. Your recovery phrase can give an attacker control over your wallet and its funds.
How to Protect Your Crypto Wallet
Always access Trezor services through the official website, verify website addresses carefully, and follow firmware update instructions from official sources. Never enter your recovery phrase into a website or share it through email, chat, or social media. Keep your computer and browser updated, and review transaction details on your hardware wallet before approving them.
Remember, a hardware wallet helps protect your private keys, but it cannot prevent every phishing attempt or stop you from approving a malicious transaction. Recognizing suspicious messages and protecting your recovery phrase are essential steps in keeping your cryptocurrency safe.
How Attackers Trick Wallet Owners Step by Step
Crypto wallet phishing attacks begin when scammers try to gain a wallet owner's trust. They may use fake websites, misleading emails, social media messages, or fraudulent security alerts to convince users to reveal sensitive information or approve unsafe transactions. Understanding how these attacks happen can help you protect your cryptocurrency.
Step 1: Creating a Fake Website or Message
Attackers create websites that look like legitimate crypto wallet services or send emails that appear to come from official support teams. These messages may warn users about account problems or suspicious activity.
Step 2: Creating a Sense of Urgency
Scammers may claim that a wallet needs an immediate security update or that funds are at risk. Their goal is to make users act quickly without checking whether the message is genuine.
Step 3: Asking for Sensitive Information
A phishing website or fake support agent may ask users to enter their wallet recovery phrase, private keys, or other sensitive information. Sharing a recovery phrase can allow attackers to access the wallet and transfer its funds.
Step 4: Tricking Users Into Approving Transactions
Some scams direct users to malicious websites that request wallet connections or transaction approvals. If users approve a harmful transaction or token permission, attackers may gain access to certain assets or move funds, depending on the permission granted.
Step 5: Stealing Crypto Assets
Once attackers obtain a recovery phrase or convince users to authorize a harmful transaction, they may transfer cryptocurrency to wallets they control. Blockchain transactions are generally irreversible, making recovery difficult.
How Can You Avoid These Attacks?
Always verify website addresses before connecting your wallet. Never share your recovery phrase with anyone or enter it into a website to resolve a security alert. Ignore unsolicited messages requesting urgent wallet actions, and verify updates through official wallet resources. Before approving a transaction, carefully check the details displayed on your hardware wallet.
How Fake Wallet Websites Steal Recovery Phrases
Fake wallet websites steal recovery phrases by tricking cryptocurrency users into entering their secret wallet information on fraudulent pages. These websites often copy the appearance of official wallet services to make users believe they are using a genuine platform. Once scammers obtain a recovery phrase, they may use it to restore the wallet on another device and access the associated cryptocurrency.
1. Creating Fake Wallet Websites
Attackers build websites that look similar to legitimate cryptocurrency wallet websites. They may copy logos, page layouts, and support information to make their websites appear genuine. Small differences in the domain name can be difficult to notice, especially when users visit the site in a hurry.
2. Spreading Fake Links
Scammers distribute links through phishing emails, social media posts, search advertisements, and messaging apps. These links may lead to fake wallet setup pages, security alerts, or fraudulent firmware update instructions. Users who click without checking the destination may unknowingly visit a malicious website.
3. Asking for the Recovery Phrase
The fake website may claim that users must verify their wallet, restore access, or complete a security check. It then asks them to enter their recovery phrase.
A recovery phrase is a set of secret words used to restore access to a cryptocurrency wallet. Anyone who obtains the phrase may be able to access the wallet's funds. Legitimate Trezor support should never ask users to disclose their recovery phrase.
4. Using the Stolen Information
After obtaining the recovery phrase, attackers may import it into a compatible wallet and gain control over the associated crypto assets. They can then attempt to transfer the funds to addresses they control. Because blockchain transactions are generally irreversible, recovering stolen cryptocurrency can be difficult.
5. Hiding the Scam
Some fake websites display a confirmation message or redirect users to a legitimate website after collecting their information. This can make users believe the process was genuine. They may not realize their recovery phrase has been exposed until they notice unauthorized transactions or missing funds.
Final Thought
Hardware wallet phishing scams work by tricking users into trusting fake websites, fraudulent support messages, and misleading security alerts. Recognizing these warning signs can help you protect your cryptocurrency from theft. Never share your recovery phrase, verify website addresses before clicking links, and carefully check every transaction before approving it. For better Trezor phishing attack crypto wallet security, always use official wallet resources and ignore unexpected requests for sensitive information. Remember, protecting your recovery phrase is one of the most important steps in keeping your crypto assets safe.