How Social Engineering Attacks Exploit Employee Trust and Put Businesses at Risk
Learn how social engineering attacks target employees, compromise business security, and what organizations can do to reduce the risk.
 safeaeon
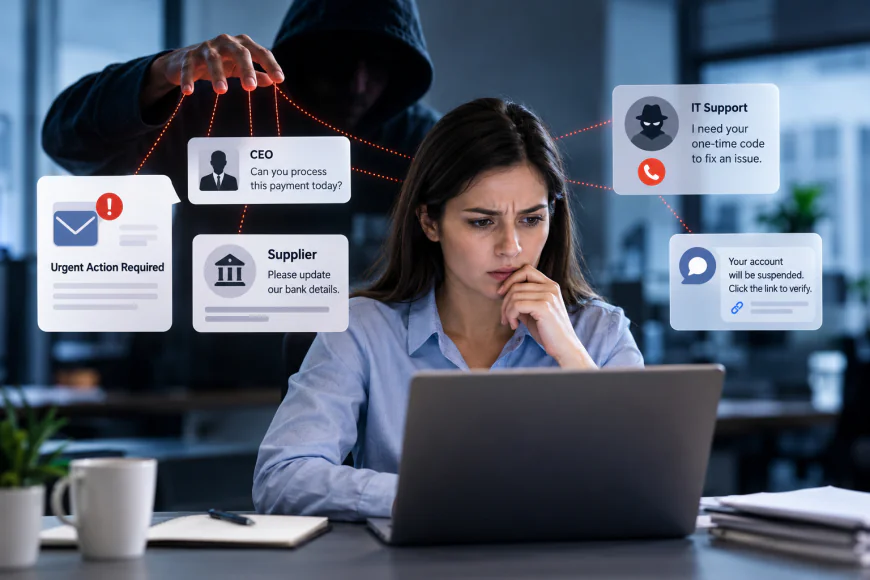
A harmless email from a manager, an urgent payment request from a supplier or a phone call, from someone claiming to be IT support may start a cyberattack.
Cybercriminals do not always need to exploit software vulnerabilities to access business systems. Sometimes cybercriminals simply convince employees to give access.
Social engineering attacks work in this way. Attackers manipulate people into sharing information approving fraudulent transactions or compromising company accounts. These attacks often involve names and convincing requests. Employees may not recognize danger until damage has already occurred.
Understanding social engineering tactics helps businesses identify activity and prevent avoidable security incidents.
What Are Social Engineering Attacks?
Social engineering is a cyberattack method that makes use of psychological manipulation to lie to people into taking moves that compromise security.
Instead of at once attacking a employer's technical defenses, cybercriminals target personnel who have access to vital structures, monetary accounts, or touchy data.
For example, an worker may acquire an e-mail that looks to come back from their organisation's IT branch. The message warns that their account can be suspended until they without delay affirm their password through a furnished hyperlink.
The hyperlink truely ends in a fraudulent website designed to capture login credentials.
Once attackers achieve those credentials, they will try and get right of entry to enterprise programs, steal personal data, or compromise additional debts.
Common Social Engineering Techniques Used Against Businesses
Cybercriminals use several methods to make fraudulent communications appear legitimate.
Phishing Emails
Phishing entails the use of fraudulent emails to lure victims into clicking dangerous hyperlinks, downloading malicious attachments, and sharing personal data.
The emails could appear to originate from banks, software vendors, co-workers, or business partners. In some instances, the phishing attack is directed at a particular employee, based on the information found from company websites and online social networking sites.
Business Email Compromise
In Business Email Compromise, the attacker assumes the identity of a trusted individual or compromises an email address to solicit illegal payments and data from the victims.
For instance, the attacker can assume the identity of a vendor and request the accounting department to change the bank account details of an outstanding invoice.
Voice Phishing and Text Message Scams
Social engineering isn't just about email.
Voice phishing (vishing) involves the use of fraudulent phone calls to trick an employee into giving up information or carrying out some unsafe action. Smishing is the text message equivalent.
For instance someone claiming to be an IT guy might call an employee and ask for a one off auth code to fix what they claim is an account issue.
Executive Impersonation
Attackers will at times pose as a senior executive in order to pressure an employee into carrying out an urgent request.
They might use pretty convincing emails, spoofed caller ID or even AI voices to make it sound genuine.
Employees who simply go by the apparent identity of the sender may well be approving of actions which they have not authorised.
How Social Engineering Attacks Affect Businesses
The effects of a social engineering attack can go beyond the employee who was first attacked.
Losses: Fake payment requests can cause direct money loss. Companies might also face costs for looking into the issue getting things back and dealing with problems.
Data exposure: Hacked accounts can let bad people see private customer details, employee data or internal papers.
Business disruption: People who get into systems might stop regular work put harmful software in or try to break in more.
Loss of customer confidence: A security problem, with information can hurt trust with customers and bring more rules to follow.
How bad these effects are depends on how much the bad person can access what information is involved and how fast the company finds out and stops the problem.
How Businesses Can Reduce Social Engineering Risks
Although social engineering assaults exploit human conduct, organizations can lessen their publicity thru clear approaches and suitable safety controls.
Build Employee Security Awareness
Employees have to recognize how phishing, impersonation, and fraudulent requests paintings.
Regular cybersecurity cognizance schooling can assist personnel understand suspicious messages, surprising login requests, and tries to create urgency.
Practical phishing simulations also can assist employees practice what they have learned.
Verify Sensitive Requests
Organizations ought to set up verification tactics for economic transactions, adjustments to banking data, password resets, and requests involving confidential data.
Employees ought to verify unusual requests thru trusted conversation channels in preference to counting on touch information furnished within the suspicious message.
Improve the Security of Email and Accounts
Email filters and authentication mechanisms will go some way towards limiting your risk from phishing emails and email spoofing.
Multi-factor authentication offers an extra layer of security against unwanted intrusion into your accounts. Phishing-resistant forms of authentication will also increase protection against credential phishing.
Restrictions should also be placed on the access of employees to systems and information that they need for their work only.
Detecting Signs of Potential Intrusion
Security monitoring will detect any signs of suspicious activity on accounts, any unexpected logins, etc.
Also, an easy-to-use reporting system should be set up so that staff members could immediately inform the security team of anything out of the ordinary.
Why Prevention Requires More Than Employee Training
Employee awareness is a way to stay safe but just teaching people is not enough to stop all social engineering attacks.
Even people who know a lot can get tricked by fake messages or by accounts that have been taken over.
Companies need security steps that help workers and make sure problems don't get too bad when mistakes happen.
Putting employee training together with email safety, passwords, controlling who has access and always watching for issues gives many chances to find and stop bad attacks.
To learn more about how attacks work what to watch for and how to stop them check out this guide about social engineering attacks on businesses, from SafeAeon.
Conclusion
Social engineering attacks be triumphant when cybercriminals convince personnel that fraudulent requests are legitimate.
An sudden electronic mail, telephone call, or charge practise can divulge a enterprise to monetary fraud, unauthorized get right of entry to, or touchy records theft.
Businesses can lessen these risks by means of helping employees understand suspicious requests, organising reliable verification approaches, and strengthening their technical security controls.
A well-organized body of workers, supported by means of effective safety methods, makes it tougher for attackers to show everyday business communications into protection incidents.