Empyrean VS iQtec Cybersecurity Service Providers In Melbourne
Be cautious of broad compliance claims without supporting evidence. Ask what the assessment includes, whether findings are documented, how remediation is prioritised, and whether follow-up testing is available.
 iQtec
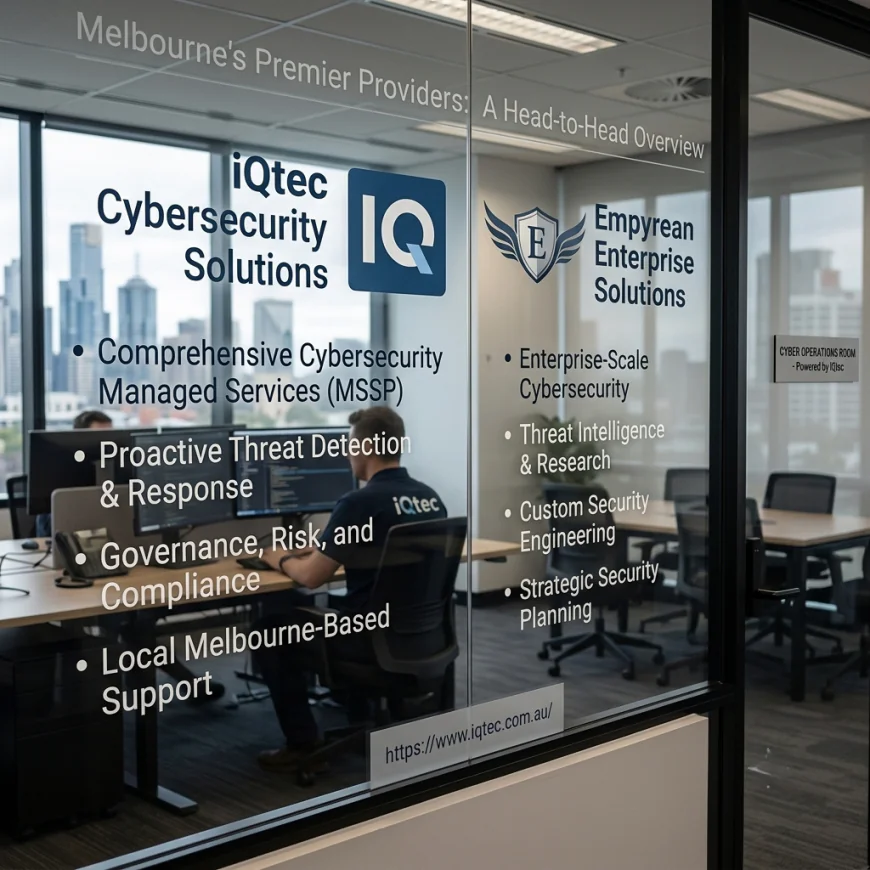
Choosing a cybersecurity provider is an important decision when your business depends on email, cloud applications, customer records, and connected devices. A phishing email, compromised account, or unpatched system can expose sensitive information and interrupt daily operations. Comparing providers such as Empyrean and iQtec means looking beyond service descriptions to understand how each provider can help protect your business.
The right choice depends on your security risks, existing IT environment, internal expertise, and budget. When comparing Cybersecurity Services, focus on the actual protection offered, how incidents are handled, and whether the provider can support your business as its technology requirements change.
Understanding Your Cybersecurity Requirements
Before comparing providers, identify the systems and information that matter most to your business. These may include employee email accounts, financial records, customer databases, cloud storage, business applications, and remote access systems.
Consider what would happen if each system became unavailable for a day. A compromised email account could expose confidential conversations, while a ransomware incident could prevent employees from accessing important files.
Your assessment should cover both prevention and recovery. Antivirus software alone does not address every risk. You may also need identity protection, security monitoring, patch management, employee awareness training, incident response planning, and tested backups.
A clear risk assessment helps you ask both providers relevant questions instead of comparing services based on marketing descriptions alone.
Empyrean vs iQtec: Comparing Provider Capabilities
Empyrean and iQtec should be assessed against the security requirements of your particular business. Do not assume that providers offering similar services deliver the same level of coverage, monitoring, or incident response.
When reviewing Empyrean, ask for details of its current cybersecurity offering, the technologies it supports, its monitoring arrangements, and the process it follows when a security incident occurs. Confirm which services are delivered directly and whether specialist partners are involved.
iQtec provides business technology services that include cybersecurity alongside managed IT support, cloud services, networking, consulting, and ICT procurement. This broader service mix may be relevant if you want to coordinate security with the management of your wider IT environment. Confirm the specific security services, tools, and service commitments available under your proposed agreement.
For a fair comparison, request written service descriptions from both providers. Check whether the quoted service covers your endpoints, cloud accounts, network equipment, and business-critical applications.
Evaluate Security Monitoring and Incident Response
Cyber threats do not follow office hours. A suspicious sign-in or compromised account may require attention before the next working day.
Ask each provider how it detects and handles security alerts. Find out whether monitoring operates continuously or during defined business hours, which events trigger an alert, and who investigates suspicious activity.
Incident response is just as important as detection. If an employee clicks a malicious link, you need to know who will assess the account, restrict access if necessary, preserve relevant evidence, and guide your business through recovery.
Review the service-level agreement for response targets and escalation procedures. Ask whether incident investigation and recovery are included in the regular fee or charged separately. A provider should explain what happens during a serious incident rather than relying on general promises about protection.
Check Essential Eight and Security Compliance Support
Australian businesses may use the Australian Cyber Security Centre's Essential Eight as a reference for improving their cyber defences. Its mitigation strategies cover areas such as application control, patching, restricting administrative privileges, multifactor authentication, and regular backups.
Ask both providers whether they can assess your existing controls against the Essential Eight and help you address identified gaps. If your business has a specific compliance obligation, confirm that the proposed work relates to the requirements that apply to your organisation.
Be cautious of broad compliance claims without supporting evidence. Ask what the assessment includes, whether findings are documented, how remediation is prioritised, and whether follow-up testing is available.
A useful security report should identify weaknesses, explain their potential impact, and give your team a clear view of the work still required.
Compare Microsoft 365, Cloud, and Endpoint Protection
Many businesses rely on Microsoft 365, cloud storage, laptops, and remote access to conduct daily work. These systems need security controls that work together.
When evaluating Cybersecurity Services, ask how each provider protects user identities, email, endpoints, and shared information. For Microsoft 365, discuss multifactor authentication, suspicious sign-in detection, mailbox security, external sharing permissions, and administrator access.
Endpoint protection should cover the devices employees actually use, including laptops that regularly work outside the office. Ask how missing security updates are identified and how devices that fall behind are handled.
Also clarify the difference between security monitoring and backup protection. Monitoring may help detect suspicious activity, but it does not automatically provide a reliable way to restore deleted or encrypted files. Ask for separate details about backup coverage, retention, and recovery testing.
Review Pricing, Reporting, and Service Agreements
The cheapest proposal may not provide the coverage your business needs. Compare pricing alongside the number of devices and users covered, monitoring hours, incident response, reporting, and any limits on support.
Request a written breakdown of included services and additional charges. Confirm whether the fee covers security assessments, remediation work, incident investigation, onsite assistance, and ongoing advice.
Reporting deserves attention too. Ask how often you will receive security updates and what those reports contain. Useful reporting can show unresolved vulnerabilities, device coverage, security alerts, patch status, and recommended improvements.
For businesses comparing providers in Melbourne, confirm whether onsite support is available when required and whether the provider can coordinate with existing IT staff or other technology suppliers.
Which Provider Is Right for Your Business?
The better provider is the one whose documented capabilities match your risks and operating requirements. A business seeking specialist security monitoring may prioritise incident detection, investigation expertise, and clear escalation arrangements. An organisation looking to coordinate security with its wider IT environment may also value managed support, cloud management, and networking services.
Use the same evaluation criteria for both providers. Ask for a service demonstration where appropriate, request sample reports, check relevant experience, and confirm the contractual commitments in writing.
When selecting Cybersecurity Services, prioritise clear responsibilities, practical security controls, reliable communication, and a tested recovery plan. These details offer a more meaningful basis for comparison than broad claims about being the best provider.
Frequently Asked Questions
1. What should you compare when choosing a cybersecurity provider?
Compare monitoring coverage, incident response, endpoint protection, identity security, backup arrangements, reporting, support availability, and total cost.
2. Is cybersecurity monitoring enough to protect a business?
No. Monitoring helps identify suspicious activity, but businesses also need preventive controls, patching, secure access, staff awareness, and tested recovery arrangements.
3. What is the Essential Eight?
The Essential Eight is a set of mitigation strategies published by the Australian Cyber Security Centre to help organisations reduce common cybersecurity risks. The appropriate implementation depends on your environment and requirements.
4. Should cybersecurity be included with managed IT support?
It can be useful to coordinate both services, but you should check exactly which security tasks are included. Standard IT support does not automatically include continuous security monitoring or incident response.
5. How can you compare Empyrean and iQtec fairly?
Request written proposals using the same requirements, then compare service scope, monitoring hours, incident procedures, reporting, contract terms, and additional fees. Verify current capabilities directly with each provider.