What Does CMMC Compliance Actually Require From You?
CMMC compliance requires more than paperwork. Learn which security controls, records, and staff steps your business needs, then build a clear action plan.
 Jack Wrtyr
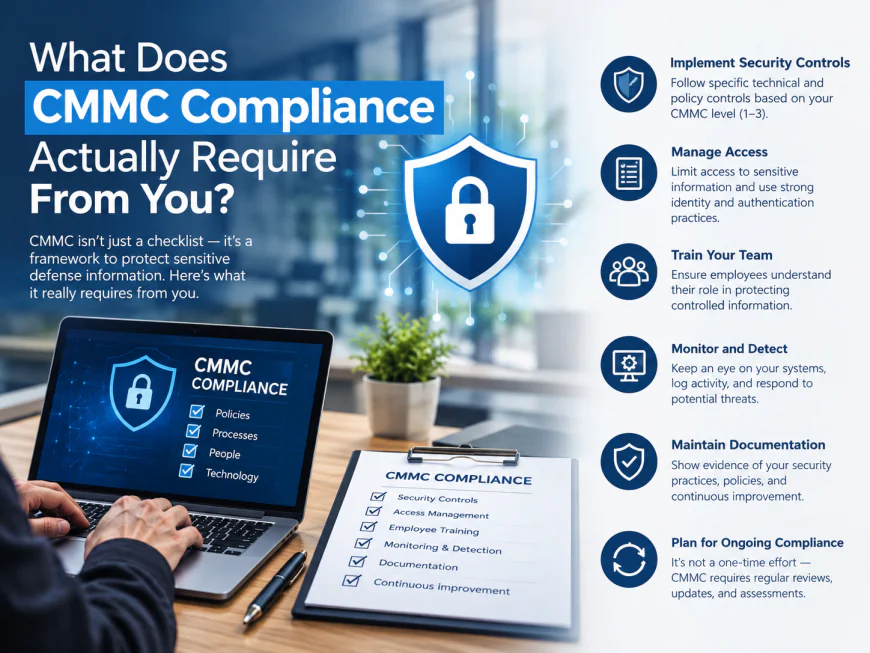
Are you bidding on DoD contracts with sensitive data? If you handle FCI or CUI, CMMC is now mandatory. The final rule is live and phased enforcement has started. Contracts already require status. This guide explains what you must do to pass. Partnering with a CMMC compliance consultant early helps you avoid delays and failed audits.
What Is CMMC Compliance In Simple Terms?
CMMC is Cybersecurity Maturity Model Certification. It verifies contractors protect Federal Contract Information and Controlled Unclassified Information. It builds on DFARS 252.204-7012 and adds verification. Self attestation alone is not enough for most programs.
The program applies to primes and subcontractors who process, store, or transmit FCI or CUI. Requirements flow down based on data handling.
Why CMMC Exists For Defense Contractors
The DoD found sensitive data was not consistently protected on contractor systems. Breaches proved the gap.
CMMC was created to enforce consistent protection across the industrial base. It uses practices from FAR 52.204-21, NIST SP 800-171, and NIST SP 800-172.
The Three Levels Of CMMC 2.0 And What They Mean For You
CMMC 2.0 has three cumulative levels. Your solicitation states the required level.
Most contractors handling CUI need Level 2. Level 1 covers FCI only. Level 3 is for critical programs.
Level 1 Foundational Requirements
Level 1 protects FCI with 15 controls from FAR 52.204-21. It requires annual self assessment and affirmation. POA&Ms are not allowed. Controls focus on basic hygiene like access limits. You must show daily use.
Level 2 Advanced Requirements
Level 2 protects CUI with 110 controls from NIST SP 800-171 Rev 2. It covers most contractors. It requires assessment every three years plus annual affirmation. Most contracts need C3PAO assessment. POA&Ms are allowed but must close within 180 days. You must upload your SPRS score before certification.
Level 3 Expert Requirements
Level 3 protects sensitive CUI from advanced threats. It includes 134 controls, 110 plus 24 from NIST SP 800-172. It requires prior Level 2 certification and a government-led assessment by DIBCAC every three years with annual affirmation.
Core Deliverables CMMC Compliance Actually Requires
Auditors check operationalization, not just paperwork. You need five deliverables.
-
First, define scope. Map where FCI and CUI live, including cloud and providers.
-
Second, build a System Security Plan. Describe how each control is implemented and who owns it.
-
Third, run a gap assessment using NIST SP 800-171A. Document gaps and create a Plan of Action and Milestones.
-
Fourth, implement controls across 14 domains. Key domains include Access Control, Audit, Incident Response, and Communications Protection.
-
Fifth, collect evidence. Keep logs, policies, training records, and baselines that prove compliance.
How The Assessment Process Works In 2026
The final rule became effective November 10, 2025. Rollout uses four phases.
-
Phase 1 started November 10, 2025. Self assessed Level 1 and Level 2 became required in solicitations.
-
Phase 2 starts November 10, 2026. C3PAO assessed Level 2 becomes required for most CUI contracts.
-
Phase 3 starts November 10, 2027. DIBCAC assessed Level 3 begins. Full enforcement completes November 10, 2028.
You must maintain compliance during performance and submit annual affirmation.
Common Gaps That Cause Failure
Scoping errors cause most failures. Over scoping increases cost. Under scoping hides CUI and creates risk.
Documentation gaps are common. Controls exist but SSP detail or evidence is weak.
External providers break compliance. If your MSP or cloud touches CUI, include it in your boundary or require its own certification.
SPRS gaps also block progress. Missing DFARS 7019 and SPRS upload prevents Level 2 certification.
How A CMMC Compliance Consultant Helps You Meet Requirements
Mapping 110 controls to processes is hard without a framework. Checklists alone do not pass. A proven method aligns existing practices to CMMC domains. It reduces rework and builds scalability.
For a practical view of how experts help streamline certification, see how an ISO certification consultant actually helps you. The right partner provides readiness reviews, internal audits, POA&M closure, and training that embeds compliance.
Sync Resource has supported 340 clients since 2009 with ISO, CMMI, and CMMC. Their process helps teams become audit ready in 90 days.
To Conclude
CMMC compliance means defined scope, implemented controls, documented SSP and POA&M, and a valid assessment. Level 1 needs 15 controls. Level 2 needs 110. Level 3 needs 134. The clock is running. C3PAO Level 2 assessments are required starting November 2026. Early preparation protects eligibility.
If you want to get certified efficiently and maintain it, working with a CMMC compliance consultant provides a clear roadmap and confidence at assessment.
FAQs
What is the difference between FCI and CUI?
FCI is nonpublic contract information. CUI needs safeguarding under federal law. Level 1 protects FCI. Level 2 and 3 protect CUI.
How long is CMMC certification valid?
Level 1 needs annual assessment. Level 2 and Level 3 status is valid three years with annual affirmation.
Do subcontractors need CMMC?
Yes, if they handle FCI or CUI for a DoD contract. Requirements flow down per 32 CFR 170.23.
What happens during a CMMC assessment?
Assessors review SSP, interview staff, check configs, and test controls against NIST 800-171A. They verify operational use.
Can I use POA&M to pass Level 2?
Limited POA&Ms are allowed for Level 2 and Level 3 and must close within 180 days. Level 1 does not allow POA&Ms.