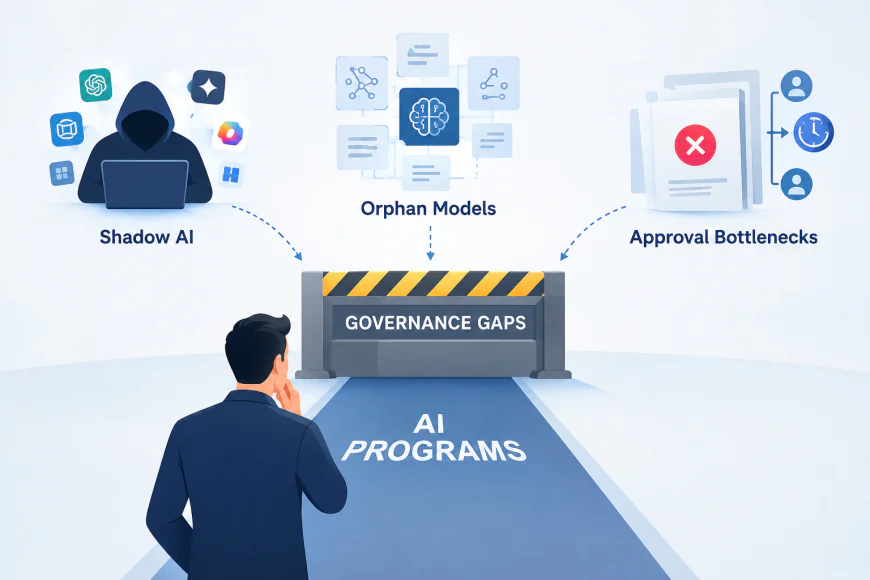
Shadow AI, Orphan Models and Approval Bottlenecks: The Governance Gaps Behind Stalled AI Programs
Stalled AI programs often trace back to shadow AI, orphan models and slow approvals. Learn the governance gaps behind them and a 90 day plan to close them.
 mobcoder ai
Ask a dozen leaders why their AI program stalled and you will hear a dozen technical explanations: the data was messy, the model was not accurate enough, the vendor overpromised. Listen longer and a pattern appears. Nobody owned the outcome, the rules were unclear and decisions took months. That is why a growing number of practitioners argue that AI transformation is a problem of governance long before it is a problem of algorithms.
This article names three specific governance gaps that quietly derail AI programs, shadow AI, orphan models and approval bottlenecks, then shows how to close each one. It also covers the standards worth knowing and a practical ninety day plan, without turning governance into a mountain of paperwork.
Quick Answer: What Is AI Governance?
AI governance is the set of policies, roles, processes and controls an organisation uses to make sure AI is built and used responsibly, legally and in line with business goals. It answers who approves a new AI use case, what data may be used, how accuracy and bias are tested, who is accountable for each system and what happens when something goes wrong.
Gap 1: Shadow AI
Shadow AI is the use of AI tools by employees without the knowledge or approval of the organisation. It rarely comes from bad intent. Someone pastes a contract into a public chatbot to summarise it, an analyst uploads a spreadsheet to a free tool, a developer connects a coding assistant to a private repository. Each action is small, and together they create real exposure.
What it costs you
-
Confidential or personal data leaves your control.
-
You cannot answer a customer or regulator who asks which tools process their data.
-
Teams build workflows on tools that may be withdrawn, repriced or changed.
-
Quality varies, because nobody tests the outputs.
How to close the gap
-
Publish a short acceptable use policy that says in plain language what is allowed, what is not, and which data must never be entered.
-
Provide approved tools so employees do not need to go around you. Banning without alternatives only pushes usage further underground.
-
Ask teams to register the AI tools they use, without blame, so you can build an honest inventory.
-
Train staff with real examples of what goes wrong.
Gap 2: Orphan Models
An orphan model is an AI system in production that nobody clearly owns. The team that built it moved on, the business sponsor changed roles, and the system keeps making predictions or generating outputs. Nobody monitors its accuracy, nobody renews its data pipeline, and nobody knows whether it still reflects reality.
What it costs you
-
Accuracy drifts as customer behaviour and data change, silently degrading decisions.
-
Security patches and dependencies are not updated.
-
When something goes wrong, nobody has authority or knowledge to fix it.
-
Costs continue without anyone checking value.
How to close the gap
-
Keep an inventory of every AI system with a named human owner, not just a team name.
-
Require a successor to be named when owners change roles.
-
Schedule reviews, for example every quarter for important systems, covering accuracy, cost and relevance.
-
Define retirement criteria so unused or underperforming systems are shut down on purpose.
Gap 3: Approval Bottlenecks
The opposite problem to shadow AI is a process so heavy that nobody wants to use it. Every request, however small, goes through the same committee that meets monthly. Teams wait, lose momentum or go around the process, which feeds shadow AI. Good governance is proportionate.
How to close the gap
Sort use cases into risk tiers and match scrutiny to risk:
-
Lower risk: internal drafting aids, meeting summaries and code suggestions. Standard policy, light review and user training.
-
Medium risk: customer facing assistants and forecasts that guide spending. Testing, privacy review, monitoring and a defined fallback.
-
Higher risk: decisions about credit, hiring, healthcare, legal rights or safety. Formal approval, bias testing, documentation, human oversight and an audit trail.
Low risk projects should be approved in days. High risk ones deserve weeks of careful review. If your approval times look the same for both, the process needs redesign.
Frameworks and Standards Worth Knowing
You do not have to invent governance from scratch. Several recognised references can guide you, and confirming which apply to you is a job for legal counsel.
-
NIST AI Risk Management Framework (AI RMF 1.0): a voluntary US framework organised around four functions, Govern, Map, Measure and Manage. It is a common starting point for US organisations.
-
ISO/IEC 42001: an international management system standard for organisations that develop or use AI, against which an organisation can be certified.
-
EU AI Act: a binding, risk based European regulation that applies in phases and affects companies serving EU markets.
-
OECD AI Principles: high level principles on transparency, accountability, robustness and human centred values.
The United States does not have a single comprehensive federal AI law. Organisations face a mix of sector rules, agency guidance and state level laws, and the details keep changing, so check current requirements for your industry.
Roles Every Governance Model Needs
-
Executive sponsor: a senior leader accountable for AI strategy and risk appetite.
-
Governance group: a small cross functional team from legal, security, data, product and the business that reviews higher risk use cases.
-
System owner: a named person responsible for each AI system's performance and compliance.
-
Data steward: responsible for data quality, access and retention.
-
Security and privacy leads: assess risks such as data leakage and prompt injection.
-
Domain experts: validate that outputs make sense in the real workflow.
In a small company, one person may hold several roles. What matters is that each responsibility has a human name next to it.
Your First Ninety Days
Days 1 to 30: Get visibility
Survey teams to find which AI tools and projects already exist, and build the inventory. Name an executive sponsor, form a small working group and publish an interim acceptable use policy.
Days 31 to 60: Set proportionate rules
Adopt a simple risk tiering model, create a short intake form for new use cases, define evaluation requirements for each tier and assign owners to existing systems, starting with the riskiest.
Days 61 to 90: Make it routine
Set up monitoring for production systems, define an incident response path, begin training and report to leadership on the inventory, risk levels and open issues. Plan the next quarter based on what you learned.
What Good Governance Looks Like in Practice
Imagine a regional insurer planning a claims triage assistant. Under weak governance, a business unit buys a tool and connects it to claims data, while legal and security hear about it months later. Under good governance, the idea goes through a short intake and is classed as medium to high risk because it touches personal and financial information. It gets a named owner. The team documents the data sources, tests accuracy on historical claims, rules that a human adjuster approves any denial recommendation, and monitors performance monthly. The launch is a few weeks later, but the system survives an audit and can scale.
Governance did not slow the project down. It prevented the far larger delays caused by late objections and rework.
Governance and Engineering Have to Work Together
Policies are only as good as the systems that enforce them. Data access controls, evaluation datasets, audit logging, version control for prompts and models and clear documentation of limitations are engineering tasks that turn policy into practice. That is why your development partner matters. A capable provider will ask about your risk tiers, data classification and approval process before proposing an architecture. To compare providers, this overview of an AI development company in USA landscape can help you shortlist firms and understand how they differ.
Delivery work such as consulting, data preparation, integration, testing and monitoring is the machinery through which governance becomes real. This explanation of AI development services shows how those activities fit together, and why governance questions belong in every project plan.
Signs Your Governance Is Working
-
Every AI system in production has a named owner.
-
Low risk requests are approved in days, not months.
-
Incidents are reported, resolved and learned from.
-
Production systems are monitored, and quality is reviewed on a schedule.
-
Employees know what they may and may not do with AI tools.
Frequently Asked Questions
What is AI governance?
It is the framework of policies, roles and controls that guides how an organisation develops, buys and uses AI responsibly, covering risk, data, accountability and compliance.
What is shadow AI?
Shadow AI is the use of AI tools by employees without organisational awareness or approval, which can expose confidential data and create compliance risk.
What is an orphan model?
An orphan model is a production AI system with no clear owner, so nobody monitors its accuracy, maintains it or decides when it should be retired.
Why do most AI projects stall?
Common reasons include unclear ownership, poor data quality, weak integration with workflows, slow approvals and no monitoring after launch. Many are governance and management problems rather than purely technical ones.
What is the NIST AI Risk Management Framework?
It is a voluntary framework from the US National Institute of Standards and Technology for managing AI risk, built around four functions: Govern, Map, Measure and Manage.
Who should own AI governance?
An executive sponsor should be accountable, supported by a cross functional group and named owners for each system. It should not sit with IT alone.
How can a small company start with AI governance?
Create an inventory of AI tools, write a one page acceptable use policy, name an owner for each system and add a simple review step for any use case involving sensitive data.
Final Thoughts
Technology will keep improving, but organisations will still struggle if nobody knows who decides, what is allowed and how results are checked. Close the three gaps: bring shadow AI into the open, give every model an owner and match approval effort to risk. Do that, and scattered experiments start to look like a dependable capability.