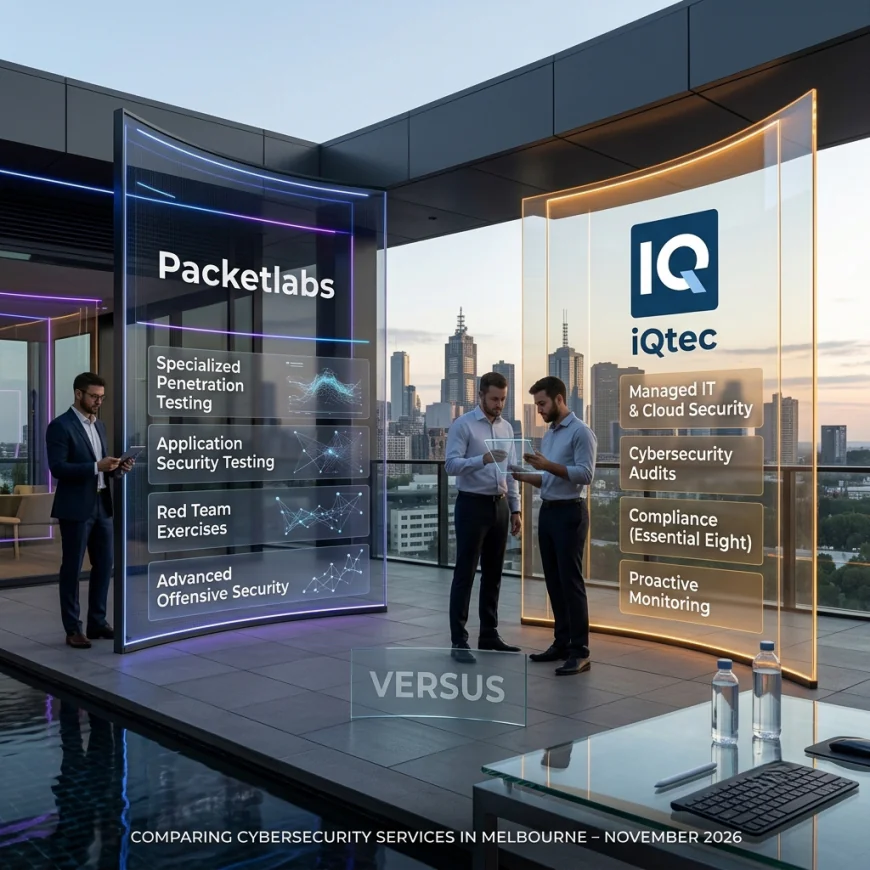
Packetlabs VS iQtec Cybersecurity Services in Melbourne - November 2026
Compare Packetlabs and iQtec cybersecurity services in Melbourne. Review penetration testing, cloud security, incident response and risk management.
 iQtec
A security weakness does not always announce itself. An outdated application, an exposed remote access account or an employee clicking a convincing phishing email can create an opening for attackers. Choosing a cybersecurity provider is therefore about more than buying security software. You need to understand how risks are identified, how weaknesses are fixed and who helps when an incident occurs.
When comparing Cybersecurity Services from Packetlabs and iQtec, start by looking at their areas of expertise. Packetlabs is known for penetration testing and offensive security assessments, while iQtec provides broader business technology services that include cybersecurity, managed IT support, cloud services and networking. These capabilities address related but different security needs.
Understanding Packetlabs and iQtec
Packetlabs is a cybersecurity company recognised for penetration testing and security assessment work. Penetration testing involves authorised attempts to identify weaknesses in systems, applications or networks before malicious actors can exploit them. Its findings can help organisations understand where their defences need improvement.
iQtec is a business technology and managed IT services provider. Its service areas include cybersecurity, managed IT support, managed cloud services, networking and communications, consulting and ICT procurement. This broader service context may suit businesses that want security considered alongside their everyday IT environment.
The important point is to compare the specific services proposed, not simply the company names. A penetration test is not the same as continuous security monitoring, and general IT support does not automatically include specialist security testing.
Start With a Clear Picture of Your Security Risks
Before requesting proposals, identify the systems and information that matter most to your business. These may include customer records, financial applications, employee accounts, cloud platforms, internal files and remote access services.
Consider how employees connect to business systems. Do they work from home? Do contractors receive access to internal applications? Are important files stored in Microsoft 365 or another cloud platform? Each arrangement creates different access and protection requirements.
A useful initial review should document:
-
Important business systems and data.
-
Devices, servers and cloud platforms in use.
-
User accounts with administrative privileges.
-
Remote access methods and external connections.
-
Existing backup and recovery arrangements.
This information gives providers a practical starting point. It also helps you avoid paying for an assessment that overlooks systems your business relies on every day.
Penetration Testing and Ongoing Security Management
One of the main differences to examine is the purpose of each service. Packetlabs' penetration testing focus may be relevant when you need an authorised assessment of how an attacker could exploit weaknesses in your environment.
A penetration test usually follows an agreed scope. The provider identifies potential vulnerabilities, tests them within authorised limits and reports the findings. You should receive clear information about the affected systems, the possible business impact and recommended corrective actions.
However, a penetration test is a point-in-time assessment. It does not replace regular patching, account reviews, endpoint protection or ongoing monitoring.
When evaluating Cybersecurity Services, ask iQtec how its cybersecurity offering addresses routine protection and how it coordinates with managed IT support. Also ask whether specialist penetration testing is included, separately available or referred to an external provider. Confirm the exact scope before assuming a particular service is part of the agreement.
What a Useful Security Assessment Should Deliver
A security assessment is valuable only when you can act on its findings. A report filled with technical terms but lacking clear priorities can leave your team unsure where to begin.
Ask the provider to explain each finding in terms of business impact. For example, an exposed administrator account may create a serious risk because it could allow unauthorised access to multiple systems. An outdated application on an isolated test device may require a different level of urgency.
A useful report should identify the affected asset, explain the weakness, describe the potential impact and recommend a practical fix. It should also distinguish urgent issues from improvements that can be scheduled over time.
Before approving a penetration test, confirm the testing scope, authorised systems, testing window and reporting process. Make sure the provider understands which systems must not be disrupted, particularly if your business operates customer-facing applications.
Cloud Security, User Access and Data Protection
Cloud platforms can introduce security gaps when permissions and settings are not reviewed regularly. An employee who changes roles may retain access to files they no longer need. A former contractor may also have an account that was never disabled.
Your security provider should help you understand how access is granted, reviewed and removed. Multi-factor authentication should be enabled for important accounts, particularly administrator accounts and remote access services.
For Microsoft 365 or other cloud platforms, ask about external sharing, suspicious sign-in alerts, administrator permissions and audit logs. You should also establish how backups are managed and whether restoration tests are performed. Cloud storage alone should not be treated as a complete backup and recovery plan.
Incident Response and Recovery Planning
Even businesses with good security controls can experience incidents. A phishing attack, compromised account or malware infection may affect operations before the cause becomes clear.
Ask both providers what happens when a suspected incident is reported. Who investigates it? Who contacts your internal team? Can affected devices or accounts be isolated? Who coordinates with software vendors or external specialists?
You should also clarify whether incident response is included in the regular agreement or charged separately. Some security engagements cover assessment and advice but do not include emergency response.
A basic response plan should identify key contacts, escalation steps, backup locations and the person authorised to make urgent decisions. Test the plan periodically so employees know what to do rather than trying to work it out during an incident.
Choosing a Provider for Your Melbourne Business
The right choice depends on your security objectives. If you need an independent assessment of vulnerabilities through authorised penetration testing, Packetlabs may be relevant to your shortlist. If you want cybersecurity considered alongside managed IT support, cloud services and networking, iQtec may be worth evaluating.
For a business in Melbourne, ask each provider to respond to the same set of requirements. Include the number of users, cloud platforms, office locations, critical applications and any compliance obligations that apply to your organisation.
Compare the proposals carefully. Check the testing scope, monitoring responsibilities, support hours, incident response arrangements and reporting frequency. Ask for separate pricing where specialist assessments or emergency services are not included.
You should also confirm who owns the assessment reports, security documentation and system records. Your business needs access to this information if you change providers or bring some IT responsibilities back in-house.
FAQs
What is the difference between penetration testing and managed cybersecurity?
Penetration testing checks for exploitable weaknesses within an agreed scope. Managed cybersecurity can involve ongoing monitoring, security administration and incident support, depending on the agreement.
Is a penetration test enough to protect a business?
No. It provides a view of security weaknesses at a particular time. Regular patching, access reviews, monitoring, backups and employee awareness remain important.
How often should a business review its cybersecurity?
Review security regularly and whenever significant changes occur, such as a new cloud platform, office network, business application or major change in employee access. The frequency of formal testing should reflect your risk and requirements.
What should you ask before hiring a cybersecurity provider?
Ask about service scope, testing methods, reporting, remediation guidance, incident response, support hours and additional fees. Get these responsibilities in writing.
Making a Well-Informed Security Choice
Packetlabs and iQtec can be considered for different parts of a business security strategy. Packetlabs' penetration testing focus may help identify weaknesses, while iQtec's wider IT services context may suit organisations looking to connect cybersecurity with everyday technology management.
Before choosing, identify the risks you need addressed and compare the actual deliverables in each proposal. The right Cybersecurity Services arrangement should give your business a clear view of its weaknesses, practical steps to reduce risk and defined support when security concerns arise.