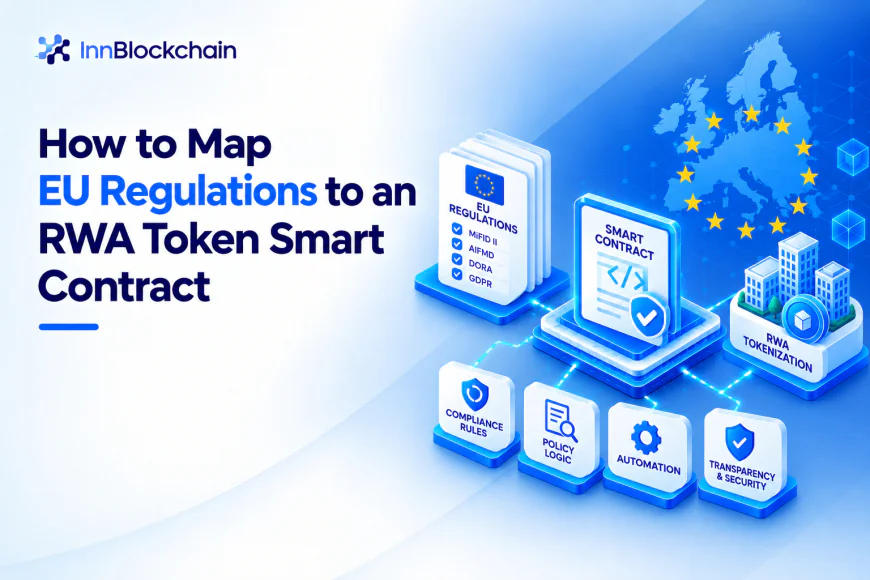
How to Map EU Regulations to an RWA Token Smart Contract
UK MiFIR drives eligibility logic; the Digital Securities Sandbox governs pilot settlement rules US The Securities and Exchange Commission The Howey Test...
 Monaliza
If you ask an engineer where GDPR lives in a smart contract, and most can't point to a line. And when you ask where MiFID II lives, the answer is often "everywhere and nowhere". A compliance narrative in a whitepaper with no corresponding function in the code. That gap is exactly what mapping closes.
Every EU regulation your platform is subject to should trace to a specific function, module, or storage decision.
What Mapping EU Regulations Actually Means for a Smart Contract
Mapping isn't a compliance summary bolted onto documentation after launch. It's a working table. One row per regulatory requirement, one column for the exact function that enforces it. This is why a modular compliance engine beats one giant approval function.
A single monolithic check can't produce a one-to-one map, and an auditor reviewing your platform will ask for that map before anything else. Each rule becomes its own addressable, upgradable module. When a regulator asks "where does Article X live?", the answer should be a function name, not a search through prose.
The Core EU Regulations an RWA Token Smart Contract Must Map
Every security tokenization platform needs to resolve these before writing the contract.
-
MiFID II maps to the identity and compliance registry. It decides who can hold the instrument and what claims they need before receiving it.
-
GDPR, Article 17 and Article 25 map to storage architecture. Personal data stays off-chain, and only a cryptographic hash or wallet reference sits on the ledger.
-
AIFMD maps to governance. Role-based access control separates whoever proposes an investment action from whoever approves it, mirroring the Directive's risk-management separation requirement.
-
DORA maps to the oracle layer. Any third-party price or valuation feed is treated as an ICT provider with its own resilience obligations.
-
The DLT Pilot Regime maps to settlement logic. It governs how a secondary market layer clears and records trades on-chain.
Mapping EU Regulations Across Jurisdictions: A Quick Reference
MiFID II and GDPR set the EU-wide baseline, but a genuine RWA tokenization development company maps beyond the EU too, since most tokenized offerings eventually touch investors elsewhere.
|
Jurisdiction |
Regulator(s) |
Where it Maps |
|
EU |
ESMA, alongside national regulators such as Germany's BaFin, France's AMF, and Luxembourg's CSSF |
MiFID II drives the identity registry; GDPR drives storage; the DLT Pilot Regime drives settlement |
|
UK |
The Financial Conduct Authority, working with the Bank of England |
Onshored UK MiFIR drives eligibility logic; the Digital Securities Sandbox governs pilot settlement rules |
|
US |
The Securities and Exchange Commission |
The Howey Test decides if the token is a security at all; transfer-agent rules map to the registry function |
|
UAE |
Abu Dhabi Global Market's FSRA, Dubai's DFSA, and the federal SCA |
ADGM's DLT Foundations regime maps directly onto the compliance-registry design |
|
Australia |
The Australian Securities and Investments Commission |
The Corporations Act maps tokenized units to existing financial-product custody rules |
|
Other non-EU markets |
Switzerland's FINMA, Singapore's MAS, and equivalent local bodies |
Same logic applies — map the local securities framework to the registry before deployment |
Mapping Transfer Restrictions to the Right Regulatory Trigger
Transfer restrictions are where the mapping gets specific, because not every blocked transfer maps to the same kind of rule.
-
A holding-period lock maps to an informative refusal — the investor can see why and when it clears.
-
A sanctions freeze maps to an opaque refusal — the same generic error every time, because disclosing more risks unlawfully tipping off the person under investigation.
-
An expired due-diligence claim maps to a fail-closed state, not a silent pass — the contract treats "unverified" and "expired" identically.
Get this mapping wrong, and you either leak information the law says you can't, or fail to block a transfer the law says you must.
Common Mapping Mistakes RWA Tokenization Development Teams Make
-
Wiring fund-level limits into the transfer hook. Concentration caps and borrowing ratios belong on the subscription and redemption functions, not on every peer-to-peer movement. It’s the transfer hook can't even measure them.
-
Collapsing every rejection into one error code. That destroys the audit trail a regulator expects and makes support tickets impossible to resolve.
-
Treating GDPR erasure as literal deletion. Erasure on a blockchain means the personal data is deleted off-chain. The on-chain hash simply becomes unresolvable.
Each of these looks like a shortcut and turns into a rebuild once flagged.
The Takeaway
A smart contract that can't show you which line enforces which regulation isn't compliant; it's unaudited. The mapping exercise is tedious, unglamorous, and exactly what separates instruments that survive regulatory scrutiny from ones that don't.
If your team is scoping tokenized RWA projects for the EU market, doing this mapping with an experienced RWA tokenization development company before a single contract is deployed is the single highest-leverage decision you'll make. Probably that’s a more relevant decision than discovering the gaps after an audit does the mapping for you.