From Chatbots to AI Coworkers: Is Your Process Ready?
Learn how autonomous AI agents work, which business processes suit them, how to set autonomy levels and guardrails, and what to ask before you invest.
 mobcoder ai
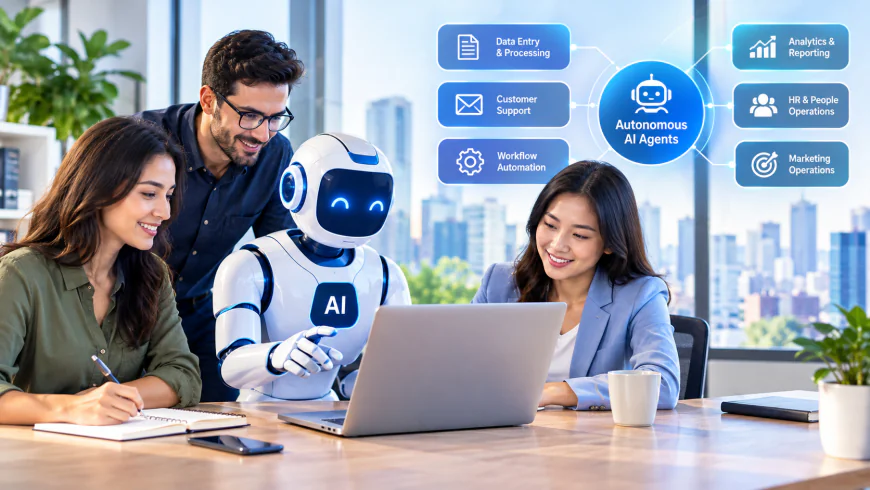
Two years ago, most companies experimenting with AI were building chatbots. Today the conversation has shifted to systems that do things: read an invoice, check it against a purchase order, flag a mismatch, message the vendor and update the ledger, all without someone shuttling data between five tabs. That shift, from answering questions to completing tasks, is what people mean by agentic AI.
The promise is real, but so is the hype. This article explains what agentic systems are, how they differ from the chatbots and automation you already have, how to decide which processes are ready, and what responsible implementation looks like. If you are weighing agentic AI development services for your business, this is the groundwork to do first.
Short answer: an agentic AI system is software that uses a language model to plan steps, call tools, and take actions toward a goal with limited supervision. It works best on well-defined, high-volume processes with clear rules, accessible systems, and a safe fallback to a human.
What Is Agentic AI, Exactly?
Agentic AI refers to systems that combine a reasoning model with memory, tools, and a control loop. Instead of producing one answer to one prompt, the system decides what to do next, uses tools such as APIs and databases, observes the result, and continues until the task is done or it needs help.
Four components show up in almost every design:
-
A model that interprets goals and decides on actions.
-
Tools that let it search, query, write, and trigger workflows.
-
Memory that keeps context across steps and sessions.
-
Guardrails that limit what it may do, with escalation to people.
Emerging standards are making tool connections easier. The Model Context Protocol, introduced by Anthropic in late 2024, gives agents a common way to connect to data sources and tools, and Google has proposed an agent-to-agent protocol for cross-system collaboration. Frameworks such as LangGraph, CrewAI, and AutoGen help teams orchestrate multi-step and multi-agent workflows.
Chatbot, Automation or Agent: Which Do You Need?
Not every problem needs an agent. Often a simpler tool is faster and cheaper.
|
Approach |
How it works |
Best for |
Weakness |
|---|---|---|---|
|
Rules-based automation |
Fixed if-then steps |
Stable, predictable tasks |
Breaks on unexpected input |
|
Chatbot or assistant |
Answers questions, drafts content |
Information access, first drafts |
Does not complete tasks itself |
|
AI agent |
Plans, uses tools, acts |
Multi-step tasks with variable inputs |
Needs guardrails and monitoring |
|
Multi-agent system |
Several specialized agents coordinate |
Complex workflows across functions |
Higher design and testing effort |
A useful rule: if the steps never change, use automation. If a person only needs information, use an assistant. If the work requires judgment across several systems, consider an agent.
Evidence and Reality Check
Industry analysts are bullish and cautious at once. Gartner has forecast that by 2028 about a third of enterprise software applications will include agentic AI, up from a tiny fraction in 2024, and that around 15 percent of day-to-day work decisions will be made autonomously. In the same period, it warned that more than 40 percent of agentic AI projects may be canceled by the end of 2027 because of cost, unclear value, or inadequate risk controls, and it called out "agent washing," where vendors rebrand chatbots as agents.
Klarna offers a real example of both sides. In 2024, the company reported that its AI assistant handled about two-thirds of customer service chats in its first month, work comparable to hundreds of agents. Later, its leadership publicly said it would emphasize human support again for quality reasons. The lesson is not that agents fail. It is that automation targets should be tied to customer outcomes, and humans should remain reachable.
Five Signs a Process Is Ready for an Agent
-
High volume and repetition. The same type of task occurs hundreds or thousands of times.
-
Clear success criteria. You can define what a correct outcome looks like.
-
Accessible systems. Data and actions are reachable through APIs or reliable interfaces.
-
Tolerable error cost. Mistakes can be caught, reversed, or reviewed before causing harm.
-
Documented rules. Policies exist, even if people apply them inconsistently.
Processes that often meet these tests include vendor onboarding, invoice matching, tier one support, IT access requests, compliance monitoring, lead qualification and internal approvals.
Processes that usually need caution include anything involving irreversible financial transfers, medical decisions, legal commitments, or hiring decisions, at least until you have strong evidence and oversight.
How Much Autonomy Should an Agent Have?
Treat autonomy as a dial, not a switch. A staged approach reduces risk while you collect evidence.
|
Level |
Agent behavior |
Human role |
Example |
|---|---|---|---|
|
1 |
Suggests actions |
Approves each one |
Drafts a refund decision |
|
2 |
Acts on low-risk tasks, asks on others |
Reviews exceptions |
Auto-resolves password resets |
|
3 |
Acts broadly within policy limits |
Audits samples |
Processes invoices under a set threshold |
|
4 |
Operates continuously with oversight |
Monitors dashboards |
Ongoing compliance scanning |
Most businesses should start at level one or two, measure accuracy, then raise autonomy where data supports it.
Designing Agents That Behave
Scope the Role Narrowly
An agent built for a defined role, with defined tools and permissions, is easier to test and trust than a general assistant with broad access. Give each agent only the access it needs, the same principle you apply to employees.
Build Human Checkpoints Where Judgment Matters
Decide upfront which decisions need approval. Escalation should carry full context so the reviewer does not start from scratch.
Log Everything
Record inputs, tool calls, decisions, and outputs. When something goes wrong, you will need an audit trail, and security and legal teams will want visibility into what the agent can access.
Test Failure Modes
Test what happens when an API returns an error, when data conflicts, when a user tries to manipulate the agent, or when a request falls outside policy. Adversarial testing, sometimes called red teaming, catches problems before users do.
Plan for Ongoing Maintenance
Models change, policies change, and workflows change. Budget for monitoring, prompt updates, and periodic architecture reviews.
Single Agent or Multi-Agent?
A single agent is easier to build and debug. Multi-agent designs help when tasks need distinct skills, such as one agent for retrieval, one for analysis, and one for execution, or when parallel work speeds things up. They add coordination overhead, shared memory challenges, and more failure points. Start simple and split only when you have evidence that one agent cannot do the job.
Where Agents Meet Other AI Capabilities
Agents rarely work alone. Many rely on generative AI development services to produce language, summaries, and structured outputs, and on retrieval systems to ground answers in company data. Teams that need role-specific assistants for support, sales, or IT can look into AI agent development services, which focus on building agents with defined decision logic, permissioned tools, and fallback paths. And because agents depend on clean data, solid integration, and monitoring, they fit best inside a broader program of AI development services that covers strategy, engineering, and operations.
A Realistic Implementation Roadmap
Weeks 1 to 2: Discover. Map candidate workflows, estimate volume, identify systems, and rank by value and risk.
Weeks 3 to 5: Prototype. Build a single-agent workflow for the top candidate with human approval on every action.
Weeks 6 to 9: Evaluate. Run the agent on historical cases and compare with human results on accuracy, time, and cost.
Weeks 10 to 12: Pilot. Release to a small group, track exceptions, and tune.
After launch: expand autonomy gradually and add new workflows only after the first is stable.
How to Judge an Agentic AI Vendor
-
Ask for a live example of an agent handling an edge case, not only the happy path.
-
Request details on evaluation methods and metrics.
-
Confirm how permissions, logging, and escalation work.
-
Check whether they are model-agnostic or tied to one provider.
-
Clarify who owns the code, prompts, and data.
-
Ask how they handle monitoring after launch.
A vendor who cannot explain failure handling probably has not seen enough production use.
Frequently Asked Questions
What is agentic AI in simple terms?
Agentic AI is software that can plan and carry out multi-step tasks on its own using tools and data, rather than just responding to a single question. It still operates within limits set by people.
How is an AI agent different from a chatbot?
A chatbot mainly converses and answers questions. An agent can take actions, such as updating records, sending messages, or triggering workflows, and it decides which steps to take to meet a goal.
Are AI agents safe for business use?
They can be, with narrow permissions, human checkpoints, logging, and testing. Risk depends on what the agent is allowed to do, so start with low-risk tasks and expand carefully.
What processes are best for AI agents?
High-volume, rules-based processes spanning multiple systems, such as support triage, invoice processing, onboarding, IT requests, and compliance monitoring.
How long does it take to build an AI agent?
A focused single-agent workflow can often reach a pilot in about two to three months, while multi-agent or heavily regulated systems take longer.
Will AI agents replace employees?
They are more likely to change roles by removing repetitive coordination work. Results vary by company, and evidence suggests human oversight remains important for quality.
What does agentic AI cost?
Cost depends on complexity, integrations, model usage, and monitoring needs. Ask for phased pricing and include ongoing inference and maintenance in your estimate.
Final Takeaway
Agentic AI is useful when it is pointed at the right work. Choose processes with clear rules and recoverable errors, start with human approval, measure against a real baseline, and raise autonomy only as the evidence supports it. The companies that benefit most will not be the ones with the most agents. They will be the ones who matched the right level of autonomy to the right job.