Enterprise AI Governance: Establishing Scalable Frameworks for Responsible AI Deployment
Discover how enterprise AI governance helps businesses deploy AI responsibly through scalable frameworks, effective risk management, regulatory compliance, and continuous monitoring. Learn how organizations can balance innovation, security, and accountability for long-term success.
 hyprforge Tech Ltd
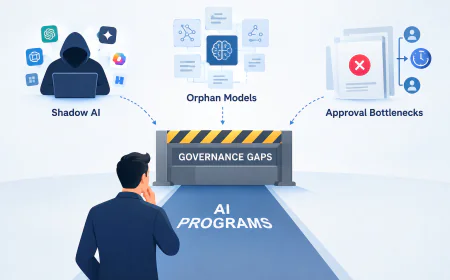
Enterprise AI adoption is moving beyond pilot projects into everyday business operations. Companies now use artificial intelligence to analyze customer behavior, automate workflows, detect fraud, and support critical decisions. As adoption grows, so does the need for clear accountability, reliable oversight, and measurable safeguards. Enterprise AI governance provides the structure organizations need to deploy AI responsibly while managing operational, legal, and reputational risks. With effective AI Governance Consulting Services, businesses can establish practical policies that support innovation without sacrificing trust.
What Is Enterprise AI Governance?
Enterprise AI governance is the combination of policies, processes, technical controls, and responsibilities that guide how an organization develops, deploys, and monitors AI systems. It helps ensure that AI applications remain aligned with business objectives, ethical standards, and applicable regulations.
Governance covers the entire AI lifecycle, from selecting training data to monitoring a model after deployment. It also defines who can approve AI projects, who reviews their risks, and who responds when something goes wrong.
A mature framework typically addresses:
-
Accountability: Assigning clear ownership for AI decisions and outcomes.
-
Data governance: Protecting data quality, privacy, and access.
-
Risk assessment: Identifying potential harm before deployment.
-
Transparency: Documenting how AI systems operate and where their limitations exist.
-
Continuous monitoring: Detecting performance changes, bias, and emerging security threats.
The objective is not to slow down development. It is to create consistent safeguards that allow teams to deploy useful AI applications with confidence.
Why Enterprises Need Scalable AI Governance Frameworks
A governance process that works for one chatbot may not be sufficient for hundreds of AI applications across different departments. As organizations expand their use of AI, informal approval processes become difficult to manage.
Scalable governance creates common standards while allowing controls to reflect the risk of each application.
Managing AI Risks Before They Escalate
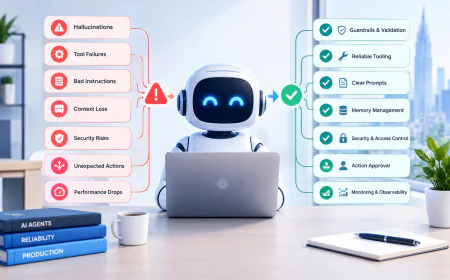
AI systems can produce inaccurate outputs, expose sensitive information, reinforce historical biases, or behave unpredictably when operating conditions change. These problems become more serious when AI influences hiring, lending, healthcare, cybersecurity, or financial decisions.
Effective AI Risk Management begins with identifying potential failures before a system reaches production. Teams should evaluate the likelihood of harm, its possible impact, and the controls required to reduce exposure.
For example, an internal tool that summarizes public documents may require basic accuracy checks and access controls. An AI system that recommends credit decisions needs stronger testing, documented human oversight, and a clear process for challenging outcomes.
Supporting Regulatory Readiness
AI regulations and privacy requirements vary by jurisdiction, industry, and application. Enterprises must understand which obligations apply to their systems instead of relying on a single policy for every use case.
Well-designed AI Compliance Solutions help organizations maintain evidence of risk assessments, testing, approvals, data handling practices, and ongoing monitoring. This documentation makes internal audits more efficient and helps teams respond to regulatory inquiries.
Core Components of a Scalable Enterprise AI Governance Model
A practical framework should combine leadership oversight with operational procedures and technical safeguards. Five components provide a useful starting point.
1. Establish Clear Ownership and Accountability
Every AI system should have an identifiable business owner and technical owner. The business owner defines its purpose and acceptable outcomes. The technical owner manages implementation, testing, and maintenance.
Larger organizations can establish an AI governance committee involving technology, legal, compliance, cybersecurity, data management, and business leaders.
Responsibilities should include:
-
Approving high-impact AI use cases.
-
Setting minimum security and testing requirements.
-
Reviewing exceptions to established policies.
-
Escalating incidents to the appropriate decision-makers.
-
Tracking governance performance across departments.
Clear ownership prevents important decisions from falling between teams.
2. Classify AI Systems by Risk
Not every AI application requires the same level of review. A risk-based classification system helps enterprises direct resources toward applications with the greatest potential for harm.
Organizations can group systems into categories such as low, moderate, high, and prohibited or unacceptable under their internal policies and applicable laws.
Each category should have defined requirements for testing, documentation, approval, and human supervision. Risk classification should also be reviewed when a model receives new data, gains additional capabilities, or begins supporting a different business function.
This approach makes governance more efficient without treating every project as equally dangerous.
3. Build Responsible Data Practices
AI performance depends heavily on the data used to train, evaluate, and operate models. Poor-quality or unrepresentative data can lead to unreliable predictions and unfair outcomes.
Enterprises should establish rules for data collection, consent where required, retention, access, and secure storage. Teams must also understand whether third-party AI providers retain submitted information or use it to improve their services.
Responsible AI Services can help organizations introduce safeguards across data preparation, model development, deployment, and ongoing evaluation.
Practical controls include data quality checks, privacy assessments, representative test datasets, and documented restrictions on sensitive information.
4. Introduce Continuous Testing and Monitoring
AI governance does not end when a model passes its initial evaluation. Model performance can change as customer behavior, input data, and operating environments evolve.
Enterprises should monitor accuracy, reliability, response quality, security, and relevant fairness indicators. Generative AI applications may also require checks for fabricated information, prompt injection, sensitive data disclosure, and inappropriate outputs.
Monitoring systems should trigger investigation when performance falls below established thresholds. Teams also need a documented rollback process so that an unreliable model can be restricted or replaced quickly.
5. Maintain Documentation and Audit Trails
Governance decisions should be recorded in a consistent format. Documentation helps teams understand why a model was approved, what limitations were identified, and which controls remain necessary.
An AI inventory is particularly useful. It should record each system's purpose, owner, provider, risk classification, data sources, approval status, and review schedule.
These records support internal accountability and provide evidence that governance controls are operating as intended.
The Role of AI Governance Consulting
Building an enterprise framework requires coordination across business, legal, security, and engineering teams. Organizations may have strong technical capabilities but lack a unified approach to risk classification, policy enforcement, or oversight.
AI Governance Consulting helps bridge these gaps by translating broad principles into actionable processes. Depending on the organization's needs, this work may include:
-
Assessing existing AI systems and governance maturity.
-
Developing policies for approved AI use.
-
Creating risk assessment and approval workflows.
-
Defining vendor evaluation and third-party model requirements.
-
Establishing audit procedures and performance indicators.
-
Training employees on responsible AI practices.
Ethical AI Consulting adds a focused review of fairness, explainability, human autonomy, and the potential effects of automated decisions on individuals and communities.
The most effective programs produce practical guidance that employees can follow. Policies should be clear enough for everyday use, with stronger review requirements reserved for higher-risk applications.
Integrating AI Governance With Enterprise Technology
AI governance works best when it is built into existing technology and business processes. Separate spreadsheets and manual approval chains can become difficult to maintain as AI adoption expands.
Enterprises can integrate governance checks into software development pipelines, model registries, identity management, security monitoring, and change management systems.
For example, an AI deployment workflow could require a completed risk assessment, security approval, documented evaluation results, and a named business owner before production access is granted.
Organizations exploring decentralized systems may also consider blockchain-based audit trails for selected use cases. A Blockchain Development Company can help assess whether distributed ledgers offer meaningful benefits for verification, provenance, or tamper-evident records. However, blockchain does not automatically make AI decisions trustworthy, and sensitive information should not be placed on an immutable ledger without careful privacy analysis.
Technology should support governance, not replace sound decision-making.
Measuring the Success of Enterprise AI Governance
A governance framework needs measurable outcomes. Simply counting completed reviews does not show whether AI systems are becoming safer or more reliable.
Enterprises can track indicators such as:
-
Percentage of AI systems recorded in the central inventory.
-
Percentage of high-risk systems reviewed before deployment.
-
Time required to approve low-risk applications.
-
Number and severity of AI-related incidents.
-
Time taken to resolve identified model issues.
-
Percentage of systems meeting documented monitoring requirements.
-
Completion rates for employee AI governance training.
These metrics should be reviewed regularly and connected to corrective actions. If approvals take too long, organizations may need better workflows. If incidents increase, they may need stronger testing or more effective monitoring.
The goal is to balance operational efficiency with appropriate safeguards.
How HyprForge Supports Responsible AI Adoption
Successful enterprise AI adoption requires more than selecting capable models. Businesses need governance structures that connect technical implementation with accountability, security, and long-term business objectives.
HyprForge can be explored as a technology partner for organizations evaluating AI governance and digital transformation requirements, providing a starting point for learning more about the company's technology capabilities and potential solutions.
Enterprises should evaluate any prospective partner against their specific requirements, including relevant experience, implementation methodology, security practices, and measurable delivery outcomes.
A scalable governance framework ultimately belongs to the organization deploying the AI. External expertise can accelerate implementation, but leadership must remain accountable for how AI systems affect customers, employees, and business operations.
Frequently Asked Questions
1. What is enterprise AI governance?
Enterprise AI governance is the set of policies, responsibilities, controls, and monitoring processes that guide how an organization develops, deploys, and manages AI systems. It promotes accountability, security, regulatory readiness, and responsible decision-making throughout the AI lifecycle.
2. Why is AI governance important for large organizations?
AI governance helps large organizations manage risks such as inaccurate outputs, data exposure, algorithmic bias, and regulatory non-compliance. It also establishes consistent standards across departments, making AI deployment easier to oversee as adoption grows.
3. What are the key elements of an AI governance framework?
The key elements include clear accountability, risk classification, data governance, security controls, model testing, human oversight, documentation, regulatory assessments, and continuous monitoring. The specific requirements should reflect the risks and intended use of each AI application.
4. How can companies implement AI governance at scale?
Companies can scale AI governance by maintaining a central AI inventory, classifying systems by risk, standardizing approval workflows, automating compliance checks, and assigning clear ownership. Integrating these controls into existing development and security processes makes governance easier to maintain.
5. How does AI governance consulting help enterprises?
AI governance consulting helps enterprises assess their current practices, identify gaps, develop policies, establish risk management procedures, and implement monitoring and audit processes. It can also help organizations prepare for relevant regulatory requirements while keeping governance aligned with business goals.