How Can Businesses Compare ISO 20000 Certification Proposals?
Businesses can compare ISO 20000 certification proposals by reviewing audit scope, certification costs, timelines, accreditation, auditor expertise, and included services to select a suitable certification arrangement.
 sahana sana
Businesses that want to enhance their IT service management process might think about getting certified to prove their processes fulfill global requirements. There are, however, a number of challenges to finding the right certification proposal like different certifiers charging different fees and prices, varying audit methodology, audit time, and/or differing levels of support. This can help the organization make a better decision on what each offer entails.
Businesses should not just consider the price of ISO 20000 Certification Proposals but also the full range of services offered. The certification value and the cost of the proposal can be impacted by factors such as accreditation by a certification body, the stage of the audit, the involvement of consultants, length of certification, surveillance audits, and extra costs. It is also helpful for a clear comparison for an organization to know what to expect during the certification process.
The Certification Scope should be checked for updates.
The first question to ask is whether the proposal is sufficiently clear to establish a scope of certification. The scope should define the IT services and operations, geographic area, department and services of the organization to be certified. Having a clearly defined scope simplifies understanding whether the certification addresses the organization's operational and business needs.
Check the credentials of the Certification Body.
The accreditation of the certification body in the proposal should be checked by the business. It is important to have certification from a well recognised and accredited organisation to ensure the audit and certification procedure is carried out in accordance with the requirements. Instead of blindly accepting a certification body's certification claim in a proposal, the organization should check the status of the certification body.
Compare Audit Stages and Methodology
Proposals and activities of ISO 20000 certification usually outline the audit segments in various ways. Businesses should verify the following components as part of the quotation: the following audit stages, preparation activities, document review, certification audit, and follow-up activities (if applicable). To be able to compare proposals fairly, it is important for organisations to understand how the audit is conducted.
Review Consultancy and Support Services
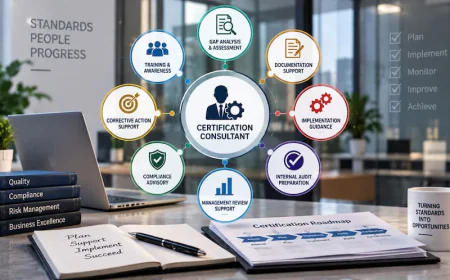
Sometimes proposals will include consultancy and/or implementation support, sometimes only certification audits. Gap assessment, documentation, guidance for implementation, employee awareness and preparation for internal audits must be carefully identified as part of the assistance that can be provided to a business. It may be easier to compare the costs if consultancy costs are split from certification costs.
Discuss Additional Costs and Pricing.
Although price is an important factor, it may not be the most economical quote. Companies need to review if travel expenses, audit day charges, certificate fees, surveillance audits, reassessment, documentation support, and other administrative costs are covered. It may be helpful to compare the total cost of certification over the certification cycle.
Check Certification Timeline
The proposed timeline should be in-line with the readiness and operation of the organization. The time that the provider estimates for preparation, auditing, corrective actions, and certification should be reviewed by businesses. If the timeline is unusually short, it may need to be closely monitored to ensure that it allows enough time for assessment and implementation to occur.
Surveillance and Recertification: Understand the concept of surveillance and recertification.
Certification is not normally a one-time activity. Post-certification surveillance audits and recertification should be considered by businesses. Proposals must include a clear outline of the schedule including costs, and certification requirements. A knowledge of these future commitments means that there will be no unexpected costs later in the day.
Assess Auditor Experience
The quality of the assessment may be affected by the experience and knowledge of the auditors. Businesses can check if the audit team has experience in similarly sized and complex organizations and IT service management systems. Having relevant sector knowledge will enable auditors to better understand the processes of the operation during the assessment.
Check the terms and deliverables of the contract
When considering accepting a proposal, businesses should check out the terms of the contract, cancellation clauses, payment plan, confidentiality, what the company is providing, and what each company will be responsible for in the event of a contract being accepted. These pieces of information combined with technical and financial considerations can guide organizations toward choosing a proposal that explicitly outlines expectations.
Conclusion
Once you have received an ISO 20000 Certification Proposal, you need to take into account a variety of factors when comparing these offers. By examining scope of certification, accreditation, audit phases, consultancy support, costs, auditor experience, and audit timelines and ongoing surveillance requirements, organizations can get a full picture of the value of each proposal.
A detailed comparison can also help companies understand the extent of hidden expenses and define the responsibilities in an agreement before entering into it. When a careful assessment of technical and commercial terms is made, it is possible to select an iso 20000 certification arrangement that fits with an organization's IT service management goals and allows for a structured approach to iso 20000 certification.