Application Security Posture Management: Uncovering Hidden Security Gaps in Modern Software Through Continuous Risk Assessment
Continuous risk assessment is therefore becoming an important part of effective application protection.
 Smith Matthew
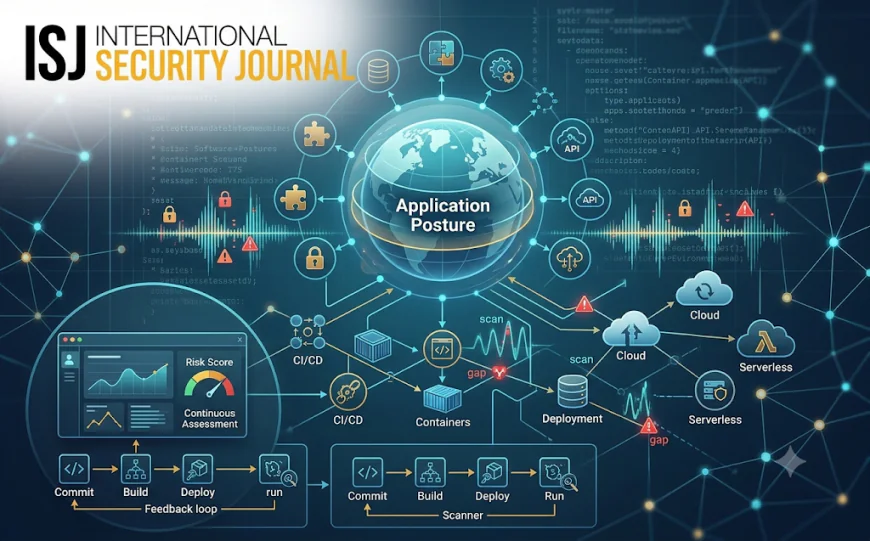
Modern software environments rely on interconnected systems, cloud-based infrastructure and complex application dependencies. While these technologies support greater efficiency, flexibility and scalability, they can also create security vulnerabilities that are challenging to detect and manage.
Potential weaknesses may exist within outdated software libraries, misconfigured settings, exposed application interfaces and inadequately monitored development environments. Even applications that have previously undergone security testing can become vulnerable as updates, integrations and underlying components evolve.
To address these changing threats, organisations need a continuous approach to identifying and evaluating application risks. Application security posture management provides greater visibility into an application's security condition, helping security teams detect weaknesses, assess potential exposure and understand how emerging vulnerabilities could affect the organisation's overall security resilience.
Understanding Hidden Weaknesses in Modern Applications
Application vulnerabilities are not always obvious.
Some weaknesses originate in source code, while others develop through software dependencies, configuration changes or connections with external services.
For example, an application may use an outdated library containing a known vulnerability. The main application code may appear secure, but the vulnerable dependency can still introduce significant exposure.
Similarly, an application programming interface may unintentionally allow access to information that should remain restricted.
These issues demonstrate why security assessments must examine more than the visible application interface.
A comprehensive assessment should consider application components, data flows, access permissions, integrations and deployment environments.
How Cloud-Native Development Introduces New Security Challenges
Cloud-native development allows applications to operate through flexible infrastructure, containers, microservices and automated deployment processes.
However, this architecture can increase the number of components that security teams must monitor.
Microservices communicate through application interfaces, while containers may be deployed and replaced frequently. Cloud resources can also be created dynamically, making asset visibility more difficult.
Misconfigured storage, excessive permissions and exposed services can create opportunities for unauthorised access.
A structured application security posture management approach can help organisations examine these interconnected environments and identify security gaps that might otherwise remain unnoticed.
Detecting Misconfigurations Before They Become Security Incidents
Misconfigurations are among the common sources of application exposure.
Examples include publicly accessible storage, unnecessary administrative privileges, insecure authentication settings and improperly configured application interfaces.
These problems may not involve a software vulnerability in the traditional sense, but they can still create significant security risks.
Regular configuration reviews help identify weaknesses and confirm that application environments follow established security standards.
Organisations should also monitor configuration changes because a previously secure application can become exposed following an update or deployment.
Continuous assessment makes it easier to identify these changes and investigate potentially unsafe settings.
Managing Third-Party Software Dependencies
Modern applications frequently rely on external libraries and software packages.
These components help developers build applications more efficiently, but they also introduce supply chain security considerations.
An outdated dependency may contain known vulnerabilities, while an insecure package update could introduce unexpected risks.
Software composition analysis helps organisations identify the components used within their applications and examine whether known security issues affect them.
However, effective dependency management requires regular monitoring and a clear process for updating or replacing vulnerable components.
By incorporating application security posture management into dependency oversight, security teams can better understand how third-party components influence application exposure.
Why Continuous Application Risk Assessment Matters
A single security assessment provides information about an application at a particular point in time.
However, software environments rarely remain unchanged.
Developers introduce updates, cloud configurations evolve and new vulnerabilities become publicly known. These developments can alter the security condition of an application.
Continuous risk assessment helps organisations maintain an updated understanding of their exposure.
It can support:
-
Regular vulnerability identification.
-
Monitoring of configuration changes.
-
Assessment of application dependencies.
-
Detection of newly exposed services.
-
Review of security control effectiveness.
-
Faster investigation of emerging risks.
This approach reduces reliance on outdated security information and helps organisations make decisions based on current application conditions.
Reducing Application Exposure Through Risk-Based Security
Identifying security weaknesses is important, but organisations must also understand which issues create the greatest potential threat.
Risk assessment should consider technical severity alongside application accessibility, exploitability and business importance.
For instance, a weakness in a publicly accessible application handling sensitive information may create greater concern than a similar issue in a restricted internal environment.
Application security posture management can help security teams connect these factors and establish practical remediation priorities.
It also supports more effective communication between security specialists and business stakeholders by explaining why particular vulnerabilities require attention.
Creating a Consistent Application Security Process
Continuous application protection requires clear processes and defined responsibilities.
Organisations should maintain an accurate inventory of applications, dependencies and supporting services. Security teams should regularly review vulnerability findings and confirm that identified issues are assigned to appropriate owners.
Development teams should also receive security guidance during application design, coding and deployment.
Useful measures include regular security testing, access reviews, dependency monitoring and configuration assessments.
Smith Matthew highlights the importance of proactive security planning and consistent risk awareness when addressing changing digital threats.
A International Security Journal provides a wider industry context for understanding how organisations are approaching resilience, technology-related risks and modern security priorities.
The Future of Continuous Application Security
As software environments become more dynamic, organisations will increasingly depend on automation to maintain security visibility.
Artificial intelligence may help correlate security findings, identify unusual application behaviour and support vulnerability prioritisation.
However, technology alone cannot guarantee application security. Effective protection still requires experienced professionals, appropriate governance and clearly defined remediation processes.
The future of application security posture management will involve combining automated assessment with human expertise to improve the speed and accuracy of security decisions.
Conclusion
Modern applications contain multiple interconnected components, making security weaknesses harder to identify through occasional assessments.
Continuous monitoring and risk assessment help organisations understand changing application conditions, detect hidden exposure and prioritise corrective action.
Application security posture management provides a structured foundation for improving application visibility and managing vulnerabilities across complex software environments.
By monitoring dependencies, reviewing configurations and strengthening development practices, businesses can reduce application exposure and build more resilient digital systems.
Frequently Asked Questions
1. What are hidden application security gaps?
They are weaknesses that may exist within software dependencies, configurations, application interfaces, access controls or interconnected services.
2. Why is continuous application risk assessment important?
It helps organisations identify new vulnerabilities and security changes as applications and their environments evolve.
3. How do cloud-native applications create security risks?
Their interconnected components, dynamic infrastructure and complex configurations can introduce additional opportunities for misconfiguration and unauthorised access.
4. What is software supply chain security?
It involves protecting the software components, dependencies, development processes and external services used to build and maintain applications.
5. How can organisations reduce application exposure?
They can conduct regular assessments, monitor dependencies, correct misconfigurations, review access controls and prioritise vulnerabilities based on risk.