AI Governance Playbook: Why AI Programs Stall at the Top
Why AI programs stall in the boardroom and how to fix it: ownership, risk tiers, policies, NIST and ISO frameworks, a practical RACI, and a 90-day plan.
 mobcoder ai
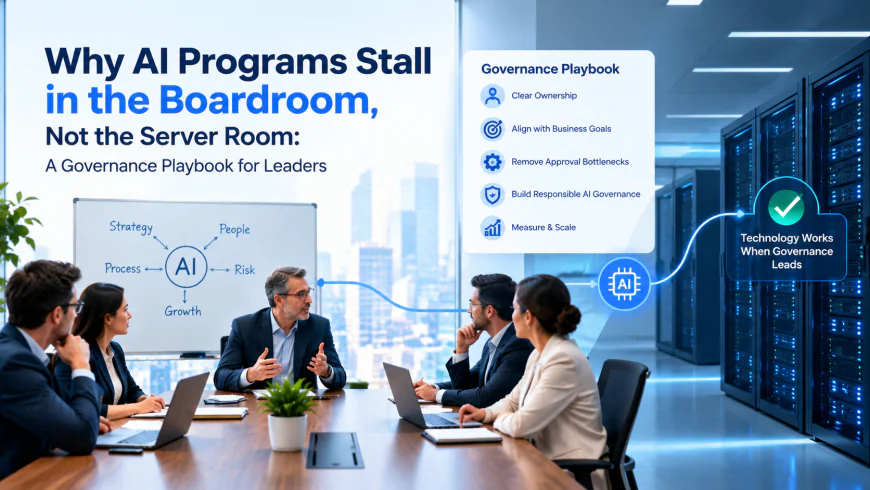
When an AI initiative fails, the post-mortem usually blames the technology. The model was not accurate enough. The data was messy. The vendor overpromised. Sometimes that is true. But in a large share of cases, the real cause is quieter: nobody decided who owns the system, what it is allowed to do, how risk is judged, or what happens when something goes wrong.
That is why many practitioners now argue that AI transformation is a problem of governance as much as one of engineering. This article lays out what that means in practice, with a framework you can adapt, real examples of what happens without it, and a 90 day plan to put the basics in place.
Short answer: AI governance is the set of decisions, roles, policies and controls that determine how AI is selected, built, deployed, monitored and retired in an organization. Good governance speeds delivery by making approvals predictable, and weak governance causes stalled pilots, shadow AI and avoidable incidents.
Why Governance Is the Bottleneck
Adoption has outpaced oversight. McKinsey's 2025 global survey on AI reported that roughly 78 percent of respondents said their organizations use AI in at least one business function. Usage is widespread, but the processes for managing it are often thin.
Three patterns show up repeatedly.
Pilots multiply without a path to production. Teams run experiments in parallel, each with its own tools and data. When one succeeds, legal, security and compliance teams see it for the first time and slow it down, sometimes for good reason.
Shadow AI spreads. Employees use public tools with company data because no approved option exists. Samsung restricted staff use of generative AI tools in 2023 after employees reportedly pasted internal code into a public chatbot, a widely cited example of how quickly well-meaning use turns into a data exposure.
Accountability is unclear. When an AI system makes a mistake, it is not obvious who answers for it. A 2024 tribunal decision in Canada held Air Canada responsible for incorrect information provided by its website chatbot, rejecting the idea that the chatbot was a separate entity. The ruling is a clear reminder that organizations own what their AI says.
Security data points the same way. IBM's 2025 Cost of a Data Breach report found that a notable minority of organizations had already experienced breaches involving AI models or applications, and that most of those lacked adequate AI access controls. Governance failures are not hypothetical.
What AI Governance Actually Includes
Governance sounds abstract, so here are its concrete parts.
|
Component |
Question it answers |
Typical artifact |
|---|---|---|
|
Ownership |
Who is accountable for each AI system? |
Named business owner and technical owner |
|
Inventory |
What AI is in use, and where? |
Central register of models, tools and vendors |
|
Risk tiering |
How risky is this use case? |
Tier definitions with required controls |
|
Policy |
What is allowed and prohibited? |
Acceptable use and data handling policies |
|
Evaluation |
Does it work and is it fair? |
Test plans, metrics, bias reviews |
|
Monitoring |
Is it still working in production? |
Dashboards, alerts, drift reports |
|
Incident response |
What happens when it fails? |
Playbooks, escalation paths |
|
Vendor management |
Can we trust third parties? |
Due diligence and contract requirements |
You do not need a large bureaucracy. A small group with real authority, clear criteria and fast decisions beats a committee that meets quarterly.
Frameworks You Can Borrow Instead of Inventing
Several public frameworks give structure.
-
NIST AI Risk Management Framework. Released by the US National Institute of Standards and Technology in 2023, it organizes work into four functions: govern, map, measure and manage. It is voluntary and widely used as a common language.
-
ISO/IEC 42001. Published in late 2023, this is an international standard for AI management systems. Organizations can use it to build and, if desired, certify a formal program.
-
EU AI Act. The European Union's law entered into force in 2024 with obligations phasing in over several years, including prohibitions on certain practices and requirements for high-risk systems. Timelines and details are being refined, so check current guidance if you operate in or sell into Europe.
-
Sector and state rules. Financial regulators, health privacy laws and state privacy statutes also apply depending on your industry and location.
Using NIST or ISO as a backbone saves time and gives auditors, customers and partners something familiar to review.
Tier Your Use Cases by Risk
Not every AI use deserves the same scrutiny. Tiering lets low-risk projects move fast while high-risk ones get more review.
|
Tier |
Example uses |
Required controls |
|---|---|---|
|
Low |
Internal drafting help, meeting summaries with no sensitive data |
Acceptable use policy, basic training |
|
Medium |
Customer-facing assistants, internal decision support |
Evaluation set, monitoring, privacy review |
|
High |
Credit, hiring, healthcare or legal decisions |
Formal validation, human oversight, bias testing, audit trail, executive sign-off |
|
Prohibited |
Uses that violate law or company values |
Not permitted |
Publish the tiers so teams know what will be asked of them before they start. Predictability is the biggest accelerator governance can offer.
Clarify Who Decides What
Ambiguity about roles kills momentum. A simple responsibility matrix helps.
|
Decision |
Business owner |
Technology |
Legal and privacy |
Security |
Executive sponsor |
|---|---|---|---|---|---|
|
Approve use case |
Accountable |
Consulted |
Consulted |
Consulted |
Informed |
|
Choose model and vendor |
Consulted |
Accountable |
Consulted |
Consulted |
Informed |
|
Approve data use |
Consulted |
Consulted |
Accountable |
Consulted |
Informed |
|
Sign off on launch |
Accountable |
Responsible |
Consulted |
Consulted |
Informed |
|
Handle incident |
Responsible |
Responsible |
Consulted |
Accountable |
Informed |
Adapt the roles to your structure, but make sure every decision has exactly one accountable person.
Governance for Agents and Generative AI
Generative AI and autonomous agents add specific concerns.
-
Hallucination. Models can state false information confidently. Ground responses in trusted data and test accuracy.
-
Data leakage. Prompts and outputs may include sensitive information. Define what data can enter which tools.
-
Prompt injection. Malicious input can manipulate a model. Test and constrain tool access.
-
Over-permissioned agents. An agent with broad access can cause broad damage. Apply least privilege.
-
Intellectual property. Check licensing for training data, outputs and third-party content.
For agents especially, log every action and decide in advance which actions need human approval.
Metrics That Show Governance Is Working
Measure the program like any other business function.
-
Percentage of AI systems in the central inventory.
-
Average time from request to approval by risk tier.
-
Number of incidents and time to resolution.
-
Share of production systems with active monitoring.
-
Percentage of employees trained on acceptable use.
-
Evaluation results tracked over time for key systems.
If approval time is shrinking while incidents stay low, governance is helping rather than hindering.
How to Choose Partners Who Support Your Governance
Most organizations rely on outside vendors for some AI work, which extends governance to third parties. Ask partners about documentation, evaluation practices, access controls, data retention and incident handling. If you are comparing options, the guide to the AI development company in USA market can help you see how providers differ in size and specialization, while an explanation of what AI development services should cover helps you check whether proposals include monitoring, security and compliance support or leave those gaps for you to fill.
A 90 Day Plan to Get Started
Days 1 to 30: Discover and assign. Build an inventory of AI tools and projects, including unofficial ones. Name an executive sponsor and a working group. Draft an acceptable use policy.
Days 31 to 60: Define and communicate. Create risk tiers, a lightweight intake process and data handling rules. Provide an approved tool so employees have a safe option. Run short training sessions.
Days 61 to 90: Operate and measure. Review your highest-risk systems, set up monitoring and incident playbooks, and begin tracking governance metrics. Publish a short report to leadership.
Afterward, review quarterly and update as laws, tools and business needs evolve.
Mistakes to Avoid
-
Writing policies nobody reads. Keep them short and practical.
-
Banning AI outright. Prohibition pushes use underground.
-
Treating governance as a one-time project. It needs ongoing ownership.
-
Leaving out frontline teams. People closest to the work spot risks early.
-
Focusing only on model risk. Data, process and people risks matter equally.
Frequently Asked Questions
What is AI governance?
AI governance is the framework of roles, policies, processes and controls an organization uses to manage how AI systems are chosen, built, used and monitored, with the goal of delivering value while controlling risk.
Why do AI projects fail even when the technology works?
Common reasons include unclear ownership, missing success metrics, late legal or security review, poor data access, and lack of a plan for monitoring and change. These are governance and operating model issues.
Who should own AI governance in a company?
Usually an executive sponsor, such as a chief data, technology or risk officer, with a cross-functional group from business, technology, legal, security and privacy. Each AI system should also have a named business owner.
What is the NIST AI Risk Management Framework?
It is a voluntary framework from the US National Institute of Standards and Technology that helps organizations manage AI risks through four functions: govern, map, measure and manage.
Do small companies need AI governance?
Yes, but scaled to size. A short policy, a list of approved tools, a named owner and a review step for customer-facing or sensitive use cases cover most of what a small firm needs.
How does governance affect speed?
Done well, it speeds delivery by making requirements clear and approvals predictable. Done poorly, it creates delays. The difference is clarity, tiering and authority to decide.
What is shadow AI?
Shadow AI is the use of AI tools by employees without organizational approval or oversight. It creates risks around data exposure and inconsistent quality, and it is best addressed by providing approved alternatives.
Final Takeaway
The servers are rarely the problem. The hardest questions in AI are about ownership, risk, accountability and trust, and those are management questions. Put a small group in charge, tier your use cases, borrow from public frameworks, measure the program and give people an approved way to work. Governance will not replace good engineering, but without it even excellent engineering struggles to reach production and stay there.