What is an AWS Sandbox and How to Use It Safely?
Learn what an AWS sandbox is, why it's essential for risk-free cloud testing, and best practices to keep your test environment secure and budget-friendly
 Vivek DB
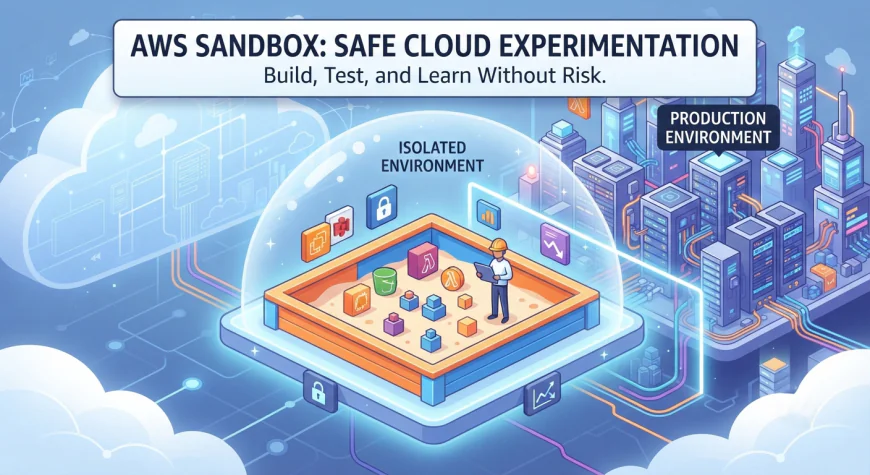
When learning or building applications in the cloud, having the freedom to experiment is crucial. However, making a mistake in a live production environment can cause downtime, data loss, or huge unexpected bills. This is where an AWS sandbox comes into play.
An AWS sandbox acts as a safe, isolated playground within Amazon Web Services. It gives developers and learners the freedom to try new ideas, test configurations, and make mistakes without risking real applications. In this article, we will look closely at what an AWS sandbox is, why it is useful, and how you can use it safely.
What is an AWS Sandbox?
An AWS sandbox is a dedicated cloud environment where users can experiment with different AWS services. Think of it like a sandbox at a playground—a bounded area where you can build whatever you want without breaking anything outside of it.
In technical terms, a sandbox is usually a separate AWS account or a strictly partitioned Virtual Private Cloud (VPC) linked to a larger organization. Because it is isolated, anything you create, modify, or delete inside the sandbox stays right there. It cannot interfere with your company’s production servers, live databases, or customer-facing websites.
Why Do You Need an AWS Sandbox?
Before cloud environments became flexible, testing new code often required expensive physical hardware or risky setups on live servers. An AWS sandbox solves many of these challenges.
1. Risk-Free Learning and Testing
When you are learning a new tool like Amazon EC2 or AWS Lambda, misconfigurations happen. You might accidentally open a security port or launch the wrong size server. In a sandbox, these errors are low-stakes learning moments rather than major company emergencies.
2. Faster Innovation
Developers move faster when they do not need to ask for permission or go through long approval chains just to test a new plugin or architecture. A sandbox empowers teams to build proofs of concept quickly.
3. Better Cost Awareness
Cloud environments cost money. Without boundaries, a forgotten database left running over the weekend can lead to a shocking bill at the end of the month. Sandboxes help teams monitor exploratory spending separate from core business operations.
How to Set Up an AWS Sandbox Safely
Even though a sandbox is meant for experimentation, it still needs structure. Leaving a sandbox completely unmonitored can lead to security vulnerabilities or runaway costs. Here is how to set up your sandbox securely.
Implement Account Isolation
The safest way to build an AWS sandbox is to create a completely separate AWS account using AWS Organizations or AWS Control Tower. By keeping the sandbox account separate from your development and production accounts, you ensure that a security breach or configuration error cannot spread to critical company infrastructure.
Establish Cost Controls and Budgets
Because experimentation can get expensive, you should always set financial boundaries.
-
Use AWS Budgets to track your spending.
-
Set up automated email or text alerts when spending crosses a specific threshold (for example, fifty dollars).
-
Restrict expensive resource types using Service Control Policies (SCPs) so users cannot accidentally spin up massive, high-end server clusters meant only for heavy enterprise production.
Best Practices for Safe Sandbox Usage
Setting up the sandbox is only half the battle. How your team uses the sandbox dictates how secure your overall cloud ecosystem remains.
Avoid Real Customer Data
One of the most golden rules of cloud safety is never to use real production data in a sandbox environment. Real customer names, emails, passwords, and payment details should never be copied into a testing account. If you need data to test an application, use synthetic or randomly generated mock data instead.
Clean Up Unused Resources
Sandbox accounts can easily turn into digital junkyards filled with old test files, abandoned databases, and forgotten virtual machines. Make it a habit to clean up your workspace. You can even write automated scripts or use lifecycle policies to shut down idle resources automatically at the end of each work day.
Conclusion
An AWS sandbox is an essential tool for anyone working in cloud computing. It bridges the gap between creativity and security, giving developers the freedom to innovate while protecting core business systems from accidental damage. By setting up proper account isolation, keeping a close eye on your budget, and avoiding real customer data, you can enjoy all the benefits of cloud experimentation with total peace of mind.