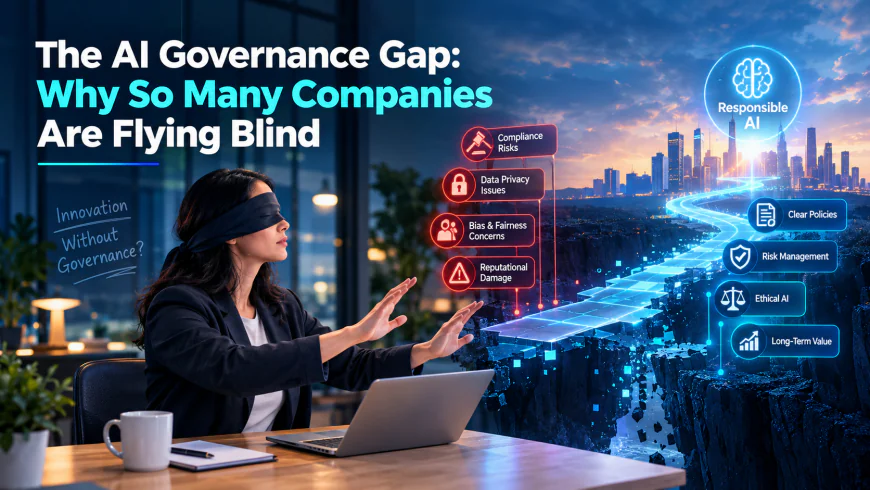
The AI Governance Gap: Why So Many Companies Are Flying Blind
Most companies deploying AI have no real governance framework in place. Here’s what the gap looks like and how to close it before it becomes a problem.
 mobcoder ai
Ask most companies how many AI tools are currently running somewhere inside their organization, and you’ll typically get a confident wrong answer. IT might know about the officially sanctioned chatbot and the vendor-integrated features in the CRM. What they usually don’t have full visibility into is the AI feature a marketing team quietly enabled inside a SaaS tool, the model an individual engineer wired into an internal script, or the AI-powered plugin a well-meaning employee installed because it made their job easier that week.
This isn’t a hypothetical risk. It’s the default state at most mid-size and large companies right now, and it’s a big part of why “AI transformation” initiatives keep stalling somewhere between the pilot and the rollout. Technology usually isn’t the bottleneck. Governance is. Companies bringing in an AI development company in New York for a serious enterprise build are increasingly asking about governance frameworks before they ask about model selection, which is a meaningful shift from where these conversations sat even a year or two ago.
What “Governance” Actually Means in This Context
Governance sounds like a compliance word, and it’s easy to dismiss as something that slows innovation down. In practice, the companies with the strongest governance frameworks tend to move faster with AI, not slower, because they’ve already answered the questions that otherwise cause projects to stall in legal review or get shut down after a scary incident.
Real AI governance covers a handful of concrete questions: Which AI tools and models is the company actually using, across every department, not just the ones IT formally approved? What data is allowed to be sent to which tools, and is anyone checking? Who is accountable when an AI system produces a wrong or harmful output, and what’s the process when that happens? How are AI-assisted decisions logged and reviewed, particularly for anything touching hiring, credit, healthcare, or other regulated or high-stakes domains?
Companies that can’t answer these questions clearly aren’t practicing risk-averse caution by avoiding AI further. They’re accumulating risk silently while getting none of the benefit of a coordinated strategy.
Why the Gap Keeps Widening
Three forces are pulling in the same direction, and together they explain why this problem tends to get worse before it gets better.
Tool proliferation is outpacing IT’s ability to track it. AI features are now embedded inside dozens of everyday SaaS products, often enabled by default or turned on with a single click by an individual employee, with no procurement process involved at all.
Business pressure to “do something with AI” often outpaces the policy work. Leadership wants visible AI initiatives, and teams respond by shipping pilots fast, frequently without anyone from legal, security, or compliance in the room until much later than would have been ideal.
Existing data governance frameworks weren’t built with this in mind. Most data governance policies were written before generative AI existed and don’t clearly address questions like whether an AI tool can be trained on customer data, or what happens when an employee pastes sensitive information into an external chatbot.
What Closing the Gap Actually Looks Like
The fix isn’t a thick policy document nobody reads. It’s a small number of concrete mechanisms, consistently enforced.
An actual inventory. Not a one-time survey, but an ongoing, lightweight process for tracking which AI tools and models are in use across the company, including the ones that show up through everyday SaaS features rather than a formal procurement process.
Data classification tied to AI use. Clear, simple rules about what categories of data can and cannot be sent to which categories of tools, communicated in plain language employees will actually remember, not buried in a fifty-page policy document nobody opens.
A defined escalation path. When an AI system produces a wrong, biased, or harmful output, there needs to be a known person or team responsible for reviewing it, and a known process for correcting it, rather than an ad hoc scramble the first time it happens.
Human review requirements matched to actual risk level. Not every AI-assisted decision needs the same level of oversight. A system drafting internal meeting notes carries very different risk than one influencing a hiring or lending decision, and the review process should reflect that difference explicitly rather than treating every use case identically.
Governance as a Competitive Advantage, Not Just a Safeguard
There’s a version of this conversation that treats governance purely as risk mitigation, a cost center that slows things down to avoid a worst-case scenario. That framing misses something important. Companies with clear governance frameworks can actually move faster on new AI initiatives, because they’re not relitigating the same fundamental questions- what data is allowed, who’s accountable, what needs review- on every single new project from scratch.
This is also increasingly a factor in how enterprise customers evaluate vendors. A company that can clearly articulate its AI governance posture during a sales process has a real advantage over a competitor that gets visibly uncomfortable when a prospect’s security team starts asking pointed questions. The idea that AI Transformation Is A Problem Of Governance, not just a technology rollout, is becoming conventional wisdom for exactly this reason: the technology is rarely what determines whether a transformation initiative succeeds or quietly stalls out.
What This Looks Like in the First Ninety Days
Companies starting from close to zero don’t need to build a mature governance program overnight, and trying to do so usually backfires by creating a process too heavy for anyone to actually follow. A more realistic sequence starts with the inventory, since nothing else can be prioritized correctly until leadership knows what’s actually running. From there, the highest-risk gaps get addressed first, typically anything touching regulated data or high-stakes decisions like hiring or credit, rather than trying to write comprehensive policy for every possible use case simultaneously.
Communication matters as much as the policy itself. A governance framework that lives in a document nobody has read isn’t really a governance framework; it’s a liability shield that will look bad in hindsight if something goes wrong. The companies that get real value from this work tend to treat the rollout as an internal communication project as much as a policy one, making sure employees actually understand the rules in practical, specific terms, like what they can and can’t paste into an external AI tool, rather than in the abstract language a formal policy document tends to default to.
By the end of the first ninety days, a reasonable goal isn’t a finished, comprehensive framework. It’s a working inventory, a clear data classification rule employees actually know about, and a named owner for AI-related incidents. Everything else can be built out from that foundation once the highest-risk blind spots are already closed.
Frequently Asked Questions
Who should own AI governance inside a company?
It works best as a cross-functional responsibility, typically anchored by someone in IT, security, or legal, but with clear input from business unit leaders who understand how AI tools are actually being used day to day, not just how they were intended to be used.
Does AI governance slow down innovation?
Done well, it does the opposite. Companies with clear governance frameworks spend less time relitigating the same risk questions on every new project, which generally lets them move faster on new initiatives, not slower.
What’s the first step for a company with no formal AI governance in place?
Start with an honest inventory of which AI tools are actually in use across departments, including tools enabled through everyday SaaS features rather than formal procurement. Most companies are surprised by what that inventory turns up.
Conclusion
The gap between AI adoption and AI governance is the quiet reason so many transformation initiatives stall after a promising pilot. Closing it doesn’t require slowing innovation down; it requires answering a small set of concrete questions, clearly and in advance, instead of discovering the answers the hard way after something goes wrong.