What Is Cybersecurity and How Does It Differ From Information Security?
What career path might be best for your goals? The best fit is based on the type of work that energizes you. If you like solving technical problems, career paths related to cybersecurity such as SOC analysis, penetration testing, security engineering and threat detection will be a good fit for you.
 Divyanshi Kulkarni
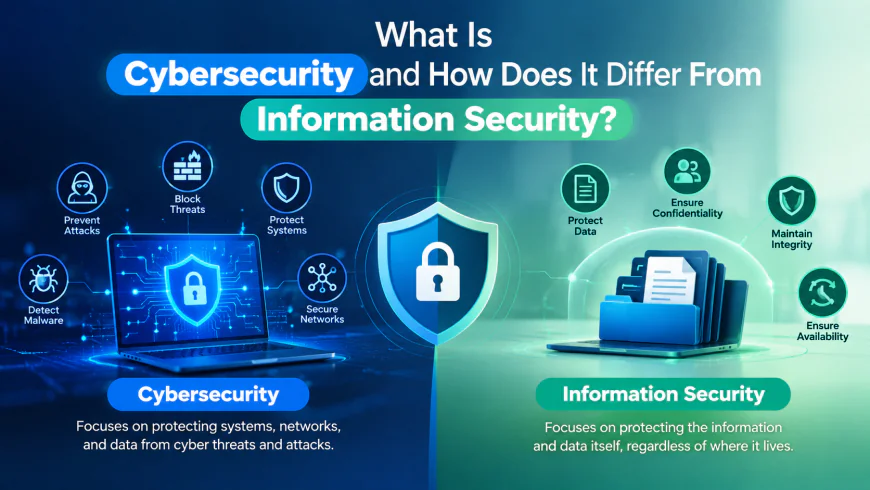
Job ads, course titles and boardroom conversations use cybersecurity and information security interchangeably, and the two fields have much in common. Their scope, responsibilities and focus differ in useful ways and those differences shape the work you would do every day.
Both fields are dealing with a wider range of risks than ever before. Cyber-enabled fraud has become CEOs’ No. 1 concern, surpassing ransomware, according to the World Economic Forum’s Global Cybersecurity Outlook 2026, with 64% of organizations now integrating attacks driven by geopolitics into their risk strategies.
Knowing where cybersecurity vs information security begins and ends will help you pick a career direction, build the right cybersecurity skills and compare the cybersecurity certifications 2027 will offer.
Cybersecurity and Information Security: A Difference in One View
The easiest way to read the table is by scope. Cybersecurity is the protection of the digital systems that hold information. Information security is the protection of the information itself, whether that information resides on a server, in an email or in a locked filing cabinet.
|
Area |
Cybersecurity |
Information Security |
|
Main emphasis |
Systems, networks and threats in the digital world |
Information security in all its forms |
|
Scope |
Most digital environments |
Digital & Physical Information |
|
Main concerns |
Attacks, malware, vulnerabilities, breaches |
integrity, availability and confidentiality |
|
Common roles |
Security analyst, SOC analyst, security engineer |
Security manager, GRC specialist, information security analyst |
|
Common controls are |
Firewall, end point security, threat detection |
Risk Management, Policies, Controls of Access |
Where Do Cybersecurity And Information Security Intersect?
Both disciplines share a common foundation, including risk management, access control, incident response, data protection, security policies and compliance. For example, a data breach investigation involves technical forensics and policy decisions about notification and recovery. That’s why many organizations have cybersecurity as a specialized area within the larger information security program, with both teams working toward the same goal.
What Does a Cybersecurity Job Really Look Like?
Cybersecurity work is practical, tech-driven. On a typical day, you could monitor networks and endpoints for suspicious activity, investigate an alert, patch vulnerabilities, run security tests, manage identity and control access, or secure cloud workloads and applications. “When something happens, you’re the one that holds it and gets systems up.”
Employers hiring for these positions want to see solid technical skills in detection, analysis and response, along with the judgment to quickly prioritize threats.
What Does an Information Security Professional Do?
Information security is an organizational and broader perspective. These people write security policies, run governance programs, assess risk, manage compliance against things like ISO 27001, classify data by sensitivity, plan for business continuity and oversee who can access what.
Typical roles are Information Security Analyst, GRC Analyst, Security Manager and Risk and Compliance Specialist and the work often involves working closely with legal, audit and business leaders.
What career path might be best for your goals?
The best fit is based on the type of work that energizes you. If you like solving technical problems, career paths related to cybersecurity such as SOC analysis, penetration testing, security engineering and threat detection will be a good fit for you.
If you like structure, policy and business risk, look toward GRC, compliance, information security and security management. Hybrid cybersecurity careers, such as security architecture, cloud security, application security and security leadership, combine both sides.
What Cybersecurity Skills Will Be More Important in 2027?
Increasingly, there is demand for threat detection and incident response, cloud security, application and API security, identity and access management, security automation and vulnerability management.
And as they grow, risk and governance skills and AI security awareness grow as well. The best profiles are technically deep, analytically minded and have a good understanding of business risk.
Cybersecurity Certification For Upskilling
Certification is one way into security work, but not the only way. A credential you wisely choose gives structure to your learning and tells employers what you know, especially when paired with real-world experience.
USCSI® Certified Senior Cybersecurity Specialist (CSCS™)
USCSI®’s CSCS™ is for those senior professionals who want to take their cybersecurity knowledge well beyond the fundamentals. The curriculum covers security governance, advanced cryptography, risk management and compliance to improve your ability to identify threats, support security operations and apply defensive practices from a broader strategic perspective.
CompTIA Cybersecurity Analyst+ (CySA+)
CompTIA Cybersecurity Analyst+ (CySA+) is a vendor-neutral intermediate certification in threat detection, security analytics, vulnerability management, and incident response.
Cybersecurity Certificate - University of Maryland Global Campus
Cybersecurity Certificate - University of Maryland Global Campus is a university-based option for structured academic learning on concepts related to cybersecurity, risk management, and defensive practices.
Cyber Security vs Information Security: Which One to Choose?
Start with the responsibilities you’d like to do most and then ask yourself whether you’d prefer a technical defense or governance focus. Think about your current experience, the needs of the industry you want to work in and where you see your career in five to ten years’ time. Finally, check the education and certification expectations for your target roles, as they often clearly indicate one path.
Cybersecurity and information security overlap quite a bit, but have different scopes. Where you go from here depends on whether you want to specialize in technical defense, broader information protection, governance and risk, or a combination of the three.
Cybersecurity and Information Security FAQs
Q. Can cybersecurity and information security professionals work in the same team?
- Yes, many organizations combine them within one security function.
Q. Does information security include physical security controls?
- Yes, it covers protecting physical records, devices and facilities too.
Q. What are common information security controls?
A. Common controls include access management, encryption, security policies, risk assessments, backups, and physical safeguards.